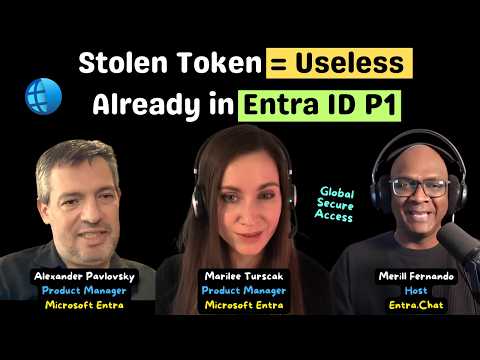
Entra ID P1: Make Stolen Tokens Useless
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Stop stolen refresh tokens with Entra ID P one using Global Secure Access compliant network and Conditional Access
Key insights
- Entra ID P1 now includes Global Secure Access (GSA) and the built-in compliant network control.
Install the GSA client on managed devices and enforce a Conditional Access policy that blocks access from outside the compliant network so a stolen refresh token or PRT cookie cannot be used from an attacker’s machine. - Token protection binds session tokens to a device using a cryptographic key.
When a service validates both the token and the device proof, copied tokens replayed from other devices fail. - Rollout follows a simple safe path: start in report-only mode, move to a small pilot group, then enable enforcement while keeping emergency or break-glass accounts excluded.
This minimizes user impact and helps troubleshoot before full enforcement. - BYOD users can get protection without installing the full client by using an Edge work profile.
This lets admins extend device-bound session protections to personal devices with minimal friction. - Agent traffic is distinguished from user traffic so policies can treat them differently.
Use a baseline rule to block sensitive actions by agents (for example, stopping an agent from deleting files the user can delete). - Copilot Studio agents can route their traffic through GSA with a single admin option, and Universal Continuous Access Evaluation (Universal CAE) now ends risky SSH sessions quickly and enforces checks based on current device state.
These controls tighten access for AI agents and interactive sessions alike.
Overview of the video
In a recent YouTube episode hosted by Merill Fernando, Microsoft product managers explained a practical way to stop stolen session tokens from being reused by attackers. They focused on the built-in capabilities available to tenants with the Entra ID P1 license and demonstrated how network-based checks make tokens unusable when an attacker tries to replay them from another device. Moreover, the guests described how the feature ties identity decisions to device and network signals so security teams can enforce more precise access controls.
The guests included Alexander Pavlovsky from the Global Secure Access feature team and Marilee Turscak, who works on secure AI adoption. Together they showed a live demo of the compliant network policy and discussed scenarios such as BYOD, Copilot agents, and responding to stolen refresh tokens or Primary Refresh Tokens (PRTs). Consequently, the episode framed the capability as an effective measure that many organizations already own in their licensing.
How the feature works
First, the presenters explained that the protection links session tokens to the device or to a verified network context so a copied token cannot be used from an attacker machine. In practice, administrators install the Global Secure Access client on managed devices and create a Conditional Access policy that requires a session to come from a compliant network. Therefore, when a token is replayed elsewhere it fails because the access request lacks the required device or network signal.
Next, the video covered source IP restoration and how the service preserves the original client signal so access checks remain meaningful behind proxies and gateways. As a result, services can evaluate both identity and network evidence before granting access. They also clarified that the protective signal does not cross tenants, which reduces the risk of false correlation or unintended exposure.
Finally, the demo showed how Universal Continuous Access Evaluation now reacts fast to changes in device state, for example ending an SSH session within minutes, and how administrators can route agent traffic through Global Secure Access. Thus, the technology improves session control both for interactive users and for automated agents such as those in Copilot Studio, when configured.
Deployment and roll-out guidance
For practical rollout, the speakers recommended a phased approach: start in report-only mode, then test with a pilot group, and finally enable enforcement while excluding emergency or "break glass" accounts. This method reduces the chance of business disruption and helps teams validate policies under real conditions. Additionally, the video emphasized the value of clear communication with end users and IT operations during each phase.
The episode also addressed BYOD scenarios and suggested using an Edge work profile to protect personal devices without installing the full client. While this option broadens coverage quickly, it comes with tradeoffs because some device-level signals are stronger on fully managed endpoints. Therefore, administrators should weigh ease of adoption against the depth of device attestation they require.
Tradeoffs and operational challenges
Although the protection strengthens security, it adds operational complexity that teams must manage. For example, requiring a compliant network can block legitimate remote access if the network or client signals are not recognized, so careful pilot testing and reliable fallback accounts are essential. Moreover, integrating identity and network teams is necessary because the solution blurs traditional boundaries between those functions.
Another challenge is accurately distinguishing agent traffic from user traffic so that automated processes do not gain excessive privileges. The speakers suggested a conservative baseline of blocking sensitive actions by agents unless explicitly allowed, but this approach can complicate automation. Consequently, organizations must balance guarding high-risk operations against preserving necessary automation and developer workflows.
Implications for security teams
Overall, the video presented the approach as a cost-effective way to reduce token replay risks for organizations that already license Entra ID P1. Security teams benefit from stronger token binding, faster session revocation, and the ability to bring agent traffic under the same policy umbrella. Meanwhile, they must plan for policy exceptions, monitoring, and the human side of change management.
In conclusion, the session offered actionable guidance and a clear demo that many enterprises can adopt without new licensing purchases. Yet, success depends on measured rollout, cross-team coordination, and a pragmatic stance on the tradeoffs between strict enforcement and user productivity. Ultimately, this network-aware identity control gives teams a practical lever to harden sessions against replay attacks while they manage complexity and maintain business continuity.
Related links
Keywords
Make stolen tokens useless Entra ID P1, Entra ID P1 token protection, Prevent stolen tokens Microsoft Entra, Revoke compromised tokens Entra ID, Entra ID session management tokens, Azure AD P1 token security, Invalidate access tokens Entra ID, Conditional Access token revocation P1