Azure Sovereign Cloud expands control choices
Microsoft Azure presented new Sovereign Cloud capabilities in Paris, giving organizations more options for controlling cloud and AI workloads.
Key insights
- Microsoft describes sovereignty as a range of choices, not a single cloud deployment model.
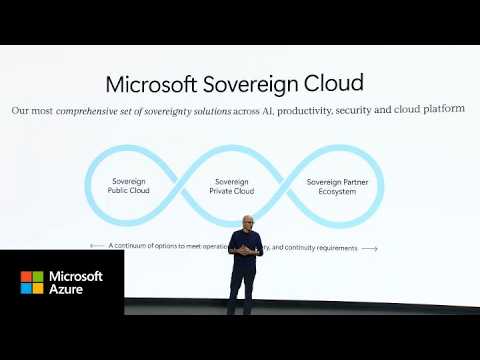
- The Sovereign Cloud continuum includes public cloud, private cloud and a partner ecosystem.
- New Sovereign Public Cloud capabilities include Data Guardian and Production Touch Ledger.
- External Key Management and Azure Confidential Clean Rooms are also named as new capabilities.
- The video presents the Sovereignty Control Panel, Foundry Local and GitHub Enterprise Local.
Microsoft Azure published a video featuring CEO Satya Nadella at the Microsoft Frontier Tour in Paris, where he presented new Microsoft Sovereign Cloud capabilities. The central message is that digital sovereignty is a set of choices across cloud environments, rather than one deployment model. For organizations weighing where workloads run and how they are controlled, the video names new public-cloud capabilities alongside private-cloud and partner options.
What's new
The video describes a sovereignty continuum spanning Sovereign Public Cloud, Sovereign Private Cloud and the Sovereign Partner Ecosystem. Microsoft’s framing is that organizations can select a level of control to suit each workload, instead of treating sovereignty as a single all-or-nothing decision. The description also highlights AI models and developer tools running alongside sensitive data.
For Sovereign Public Cloud, Microsoft names four capabilities: Data Guardian, Production Touch Ledger, External Key Management and Azure Confidential Clean Rooms. The video description identifies them as new capabilities, but does not explain their technical configuration, eligibility or rollout details. Their inclusion signals that Microsoft is addressing operational oversight, access records, key management and protected data collaboration as parts of its sovereignty portfolio.
The presentation also points to the Sovereignty Control Panel, Foundry Local and GitHub Enterprise Local. In the research notes, the control panel is described as a place to view sovereignty controls and gaps, while Foundry Local and GitHub Enterprise Local are associated with locally run or disconnected environments. The published video description itself names these products but provides limited implementation detail.
Why it matters
For IT administrators and architects, the portfolio approach offers a way to assess different control needs by workload. A highly sensitive system might call for a different environment or operational arrangement than a less restricted one. The video’s key point is that organizations can consider public cloud, private cloud and local partners as parts of the same sovereignty strategy.
That framing is relevant to organizations evaluating cloud and AI use in Europe, especially where data handling, privileged access and operational control are central to their requirements. The named capabilities suggest that sovereignty is not presented only as a question of where data is stored. It also involves controls around access, keys, operations and AI workloads.
For developers and AI teams, Foundry Local and GitHub Enterprise Local are notable because the presentation connects local infrastructure with AI models and development tools. This may matter to teams whose environments need to keep those tools close to sensitive data. However, the available material does not set out supported configurations or say which organizations can use each option.
The video does not state licensing requirements, pricing, or a general availability schedule. Administrators should therefore treat it as an overview of Microsoft’s direction and named capabilities, not as enough information to plan a deployment or determine whether a particular tenant can use them.
How it works
Microsoft presents the approach as a selection of controls and environments rather than a single product switch. The practical decision path implied by the presentation is to identify workload requirements, choose an appropriate part of the continuum, and then consider the relevant sovereignty controls.
- Assess the workload. Determine the level of control needed for its data, operations and AI use. The presentation does not provide a formal assessment framework.
- Choose an environment. Consider Sovereign Public Cloud, Sovereign Private Cloud or the Sovereign Partner Ecosystem, according to the workload’s requirements.
- Review the controls. The named capabilities include Data Guardian, Production Touch Ledger, External Key Management and Azure Confidential Clean Rooms. The video description does not map each capability to a specific workload or configuration.
- Consider local tools. The presentation names Foundry Local and GitHub Enterprise Local alongside the Sovereignty Control Panel as part of the wider set of options.
In the research notes, Data Guardian is described as involving European partner oversight of qualifying remote access by Microsoft engineers to production systems. Production Touch Ledger is described as an audit record for privileged access. External Key Management is associated with customer control of encryption keys. These descriptions provide context, but the video’s short published summary does not give enough detail to validate deployment mechanics or customer responsibilities.
Limitations and open questions
The published material is an overview, not a technical guide. It does not explain the detailed architecture of the four named public-cloud capabilities, the requirements for using them, or how they interact with existing Azure controls. Nor does it specify which features are available now, in preview, or planned for later.
Important procurement and operations questions remain unanswered in the material: licensing, pricing, regional scope, service-level commitments and migration steps are not stated. The description also does not define what qualifies as a sensitive workload or show a worked example of choosing among the three parts of the continuum. Organizations should verify those points against current product documentation before making deployment decisions.
Sources
Frequently asked questions
What does Microsoft mean by a sovereignty continuum?
The video describes choices across Sovereign Public Cloud, Sovereign Private Cloud and the Sovereign Partner Ecosystem. It presents these as options for selecting a level of control for different workloads.
Which new Sovereign Public Cloud capabilities does Microsoft name?
The video names Data Guardian, Production Touch Ledger, External Key Management and Azure Confidential Clean Rooms. It does not provide detailed technical setup instructions.
Are the capabilities generally available, and what do they cost?
The material does not state availability, licensing or pricing. Those details need to be confirmed in current Microsoft product documentation.