Security
Oct 2, 2026 10:19 AM
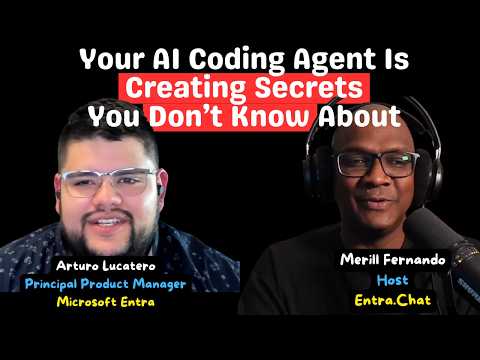
AI Coding Agent: Hidden Secrets Revealed
by HubSite 365 about Merill Fernando
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
AI agents create secret sprawl; Microsoft Entra Agent ID and workload identities on Azure enable secretless identity
Key insights
- AI coding agents can create or expose credentials without developers noticing.
They often generate placeholders, write tokens into configs or prompts, or suggest insecure patterns that cause secret sprawl. - Secret failure modes: secrets break when they are leaked, expired, or become orphaned with no owner.
Treat placeholder values like "your-api-key-here" as bugs until you replace them with secure handling. - Managed identity removes stored credentials from code by issuing tokens at runtime instead of keeping secrets in apps.
Use DefaultAzureCredential or certificate-based auth in production and resolve secrets at runtime rather than embedding them. - Workload identity federation extends secretless access across clouds and services, covering AWS, GCP, Azure Arc and some AI vendors.
Open standards like SPIFFE and ID-JAG enable agents to cross environments without secrets or interactive prompts. - Practical steps: never hardcode secrets or paste keys into prompts; store credentials in Azure Key Vault, GitHub Secrets, PasswordVault, or environment variables.
Always audit AI-generated code for hardcoded secrets, unsafe logging, and insecure config values before deployment. - Avoid secrets is the single rule for agent builders: prefer managed or federated identities and vault-backed storage to reduce risk.
Microsoft still allows client secrets for compatibility, so identify and remove them where possible to prevent accidental exposure.
Keywords
AI coding agent secrets, AI code assistant privacy, coding agent data leakage, AI developer tool risks, Copilot privacy concerns, autonomous coding agent security, AI code generation vulnerabilities, hidden AI coding behaviors
HubSite 365 Apps