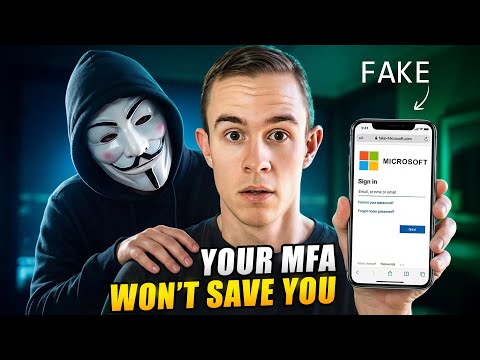
MFA 2026: Hardening Against New Hacks
Microsoft expert: stop AiTM phishing, protect sessions with phishing-resistant MFA, Windows Hello and Azure AD controls
Key insights
- Adversary-in-the-Middle (AiTM): The video shows how attackers use proxy relays to sit between a user and the login page, capturing MFA prompts and session tokens in real time.
AiTM attacks let attackers complete a login while the user thinks they signed in normally. - MFA limitations: MFA protects the initial sign-in event but often does not protect the active session, so stolen or relayed tokens can keep access open.
Attackers exploit prompt fatigue, social engineering, legacy flows, and misconfigured exemptions to bypass MFA. - token replay: Attackers capture authentication tokens or cookies and replay them to create valid sessions without redoing MFA.
The video includes a real-world example where session replay allowed sustained access despite MFA being enabled. - phishing-resistant MFA: The recommended defenses are FIDO2/passkeys, hardware keys, Windows Hello, and certificate-based or device-bound keys, which stop most relay attacks.
The presenter advises retiring SMS, voice, and email codes because they remain easy to phish or intercept. - Conditional Access: Use Conditional Access to enforce MFA everywhere, apply continuous access evaluation, and remove broad exceptions or break-glass accounts.
Defend CLI, SDK, IaC, and admin planes with the same policies you use for portals to close gaps. - workload identities: Replace service accounts and legacy username/password flows with managed identities, client credentials, and short-lived certificates or keys.
Combine workload identity migration, tighter logging, and strict rotation to reduce attack surface and make MFA effective in 2026.
The newsroom reviewed a recent YouTube presentation by Nick Ross [MVP] (T-Minus365) that explains why multi-factor authentication remains vulnerable and how he would redesign MFA for 2026. In the video, Ross demonstrates how modern adversaries use Adversary-in-the-Middle attacks to bypass protections that defenders often assume are sufficient, while also laying out practical architectural changes organizations should adopt. Consequently, the piece serves both as a technical breakdown and a policy roadmap, aimed at security teams responsible for Microsoft 365 environments. This article summarizes the core arguments and explores the tradeoffs and implementation challenges Ross highlights.
How AiTM Phishing Works Behind the Scenes
Ross walks viewers through the mechanics of an AiTM phishing attack, showing how a proxy or session-relay tool intercepts credentials and one-time factors in real time. Attackers forward the sign-in flow to victims, capture responses such as push approvals or codes, and then replay tokens to complete a legitimate session from their own endpoint. Thus, even when an organization has layered MFA on the login event, the attacker can inherit an active session and operate until it expires or is revoked. The video emphasizes that MFA often protects a point-in-time login but does not automatically protect an ongoing session unless additional controls are used.
Why Modern MFA Deployments Still Fail
Ross identifies several recurring failure modes, starting with human factors like prompt fatigue and social engineering that lead users to approve malicious approvals. He also points out technical gaps, including legacy authentication flows, non-interactive service accounts, and misconfigured Conditional Access policies that create exceptions attackers can exploit. Moreover, supply-chain compromises or stolen long-lived credentials enable attackers to mint tokens or escalate privileges, which defeats user-level MFA unless other defenses intervene. Finally, the presenter notes that inconsistent enforcement across portals, SDKs, and command-line tools leaves practical gaps that threat actors exploit.
These weaknesses matter because many enterprises still rely on weak second factors such as SMS, voice, or email, which attackers can phish or socially engineer, and because automation needs often push teams to create exceptions. Ross underlines that changing one part of the authentication ecosystem without addressing the broader “session and automation” problem will produce brittle results. Therefore, defenders must consider both human-centric authentication and machine-to-machine identity models when planning upgrades. In short, patching individual vectors helps but does not remove systemic risk.
Designing MFA for 2026: Phishing Resistance and Device Binding
To counter these threats, Ross recommends a shift to phishing-resistant factors such as FIDO2 hardware keys, platform passkeys, certificate-based authentication, and continuous device attestation that tie identity to a specific device. He argues that these approaches deny attackers the ability to replay intercepted tokens because the private key material never leaves the device and cryptographic challenges require the original key. Additionally, Ross advocates enforcing MFA across all control planes — portals, APIs, CLI, and infrastructure-as-code — so that automation and admin operations no longer create security islands. Together, these measures raise the cost for attackers and remove many simple bypass paths.
Tradeoffs and Practical Challenges of Migration
Implementing phishing-resistant MFA carries practical tradeoffs: it improves security substantially but increases operational complexity during migration, especially for service accounts, legacy applications, and third-party integrations. Ross stresses that moving non-interactive workloads to managed identities or certificate credentials reduces risk, yet organizations must invest time to modify code, update libraries, and validate deployments, which can disrupt automation if rushed. Furthermore, the human side matters, because user onboarding to hardware keys or passkeys requires training and recovery mechanisms for lost devices, so administrators must balance security gains against user friction and support costs.
Actionable Steps and Recommendations
Ross provides clear, actionable recommendations that security teams can implement progressively, including retiring SMS, voice, and email as MFA factors and enforcing phishing-resistant methods for all interactive accounts. He also recommends removing broad Conditional Access exemptions, retiring legacy username-password flows, and protecting break-glass accounts with strict controls to prevent over-permissive escapes. Finally, he emphasizes adopting defense-in-depth by combining strong authentication with device compliance checks, session lifetime limits, token revocation workflows, and continuous monitoring so that attackers cannot pivot even if they succeed on one front.
In conclusion, the video by Nick Ross [MVP] delivers a balanced assessment that recognizes the benefits of modern MFA while also calling out the operational hurdles organizations must solve. His 2026 design centers on phishing resistance, consistent enforcement, and migration of machine identities, and it acknowledges that real security requires both technical controls and careful change management. For security teams, the message is clear: evolving MFA is no longer optional, but doing so successfully means planning for tradeoffs, reskilling operations, and treating sessions and automation as first-class security problems.
Keywords
MFA bypass 2026, why MFA fails, multi-factor authentication vulnerabilities, how MFA gets hacked, implement MFA 2026, phishing-resistant MFA, passwordless authentication 2026, adaptive MFA best practices