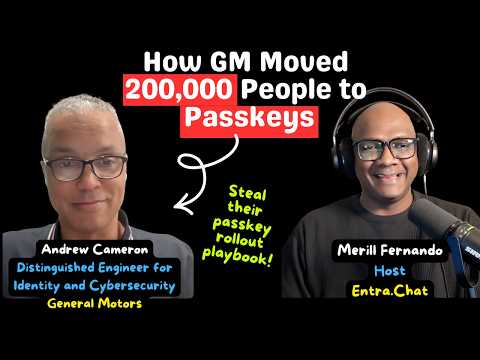
Passkey Playbook: GMs 200K Rollout
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
GM passkey playbook shows Windows Hello fast path to Microsoft Entra ID with Conditional Access and Azure PIM
Key insights
- Passkeys are now the enterprise default in Microsoft Entra ID, with Microsoft making passkeys the default on 1 September 2026 and retiring Microsoft-provided SMS/voice MFA on 1 February 2027.
General Motors rolled this change to about 200,000 people and treated the timeline as fixed—so planning for day-one access is essential. - GM used Windows Hello as the fast path and enabled roughly 100,000 users without phones; Platform SSO extended the same approach to Mac devices.
Leverage managed devices first to get rapid, low-friction coverage. - Start with privileged accounts and automation: require passkeys for admins via Azure PIM, then use Conditional Access as the rollout engine by piloting, running audit mode, and progressively adding apps and groups.
Targeting the largest apps often gets you to ~80% coverage fastest. - Watch onboarding and replacement gaps: GM found default SMS onboarding broke day-one access, so they issue a Temporary Access Pass and register a strong method immediately; new-phone flows also need redesign.
Decide early on synced vs device-bound passkeys and build recovery paths. - Handle edge cases before they block rollout: guest accounts can be blocked if their home tenant lacks passkeys; factory floors require hardware keys or custom non-password methods; VDI often needs certificate auth or Azure Virtual Desktop SSO.
Include unmanaged devices, network location, and device posture in risk rules for call centers and contractors. - Operational playbook: monitor, target, measure—run small pilots, audit sign-ins, expand by high-value apps, and track coverage metrics.
Know every authentication method in use before retiring SMS and keep the process iterative and documented to avoid lockouts.
Overview of the YouTube briefing
In a recent YouTube interview hosted by Merill Fernando, Andrew Cameron, Distinguished Engineer for Identity and Cybersecurity at General Motors, described how GM deployed passkeys to roughly 200,000 users. The conversation focused on practical steps, unexpected problems and the tradeoffs the company weighed while moving away from legacy multi-factor options. Importantly, Microsoft plans to make passkeys the default in Microsoft Entra ID on 1 September 2026 and to retire Microsoft‑provided SMS and voice MFA on 1 February 2027, which framed much of GM’s urgency and decisions. The video offers a clear case study for any large organization planning a similar migration.
What worked: practical fast paths and policy levers
GM found a fast route to broad coverage by using managed endpoints as credentials, with Windows Hello enabling about 100,000 people without requiring roaming keys or phones. Similarly, GM extended the same device-based approach to Apple devices using Platform SSO, which reduced the complexity for already-managed workstations. They also prioritized privileged accounts first by forcing stronger authentication through Azure PIM, ensuring admin roles were secured early in the rollout. In parallel, Conditional Access acted as the deployment engine — starting with a small pilot, moving to audit mode and then adding apps and groups to scale safely.
Challenges that surprised the rollout team
Not all problems were technical; some were procedural. GM discovered that default onboarding used SMS as a bootstrap method, so removing SMS inadvertently cut off new hires on day one until GM introduced a Temporary Access Pass and registered a strong method immediately. Device replacement also caused trouble because a new phone could default back to SMS, so the device-replacement path had to be redesigned rather than adjusting only the sign-in policy. The guest and partner ecosystem proved another major friction point: suppliers and contractors can be blocked if their tenant has not enabled passkeys, a situation that requires coordination rather than a single tenant fix.
Balancing design choices: synced vs device-bound passkeys
One central tradeoff was whether to use synced passkeys or keep keys device-bound. Synced keys improve cross‑device mobility and help users who change or lose devices, but they expand the attack surface and require robust cloud protections. Device-bound keys reduce risk by tying credentials to a specific endpoint, which simplifies some compliance and attestation requirements, yet they make device replacement and roaming more complex for users. GM's approach mixed both models where appropriate and emphasized understanding every authentication path before retiring older methods.
Special environments: factories, call centers and virtual desktops
GM’s workforce includes people without phones or keyboards on factory floors, which meant a traditional passkey flow would fail for those users. The team developed custom non-password methods and used hardware keys for robots and automated systems, acknowledging that one-size-fits-all does not work for industrial contexts. Call-center staff on unmanaged devices required incorporating device posture and network location into risk evaluation, while VDI users needed certificate-based authentication or Azure Virtual Desktop SSO after SMS was removed. Each environment demanded a tailored mix of tools and policies rather than a single universal setting.
Operational lessons and final guidance
GM’s playbook offers pragmatic advice: treat managed endpoints as credentials when possible, secure privileged roles first, and use Conditional Access to pilot and expand methodically. Targeting the largest, most-used applications early accelerates coverage to about 80 percent, but teams must also plan onboarding, device-replacement flows and guest access to avoid day-one lockouts. Monitoring, measuring and keeping an inventory of authentication methods are essential, as is readiness to unwind prior assumptions like AAGUID attestation once synced passkeys arrive. Ultimately, the rollout shows that technical capability must be paired with operational planning to avoid service disruption.
Keywords
enterprise passkey adoption, passkey deployment at scale, general motors passkey rollout, passkey security best practices, enterprise passwordless strategy, employee passkey implementation, large scale identity management, passkey migration guide