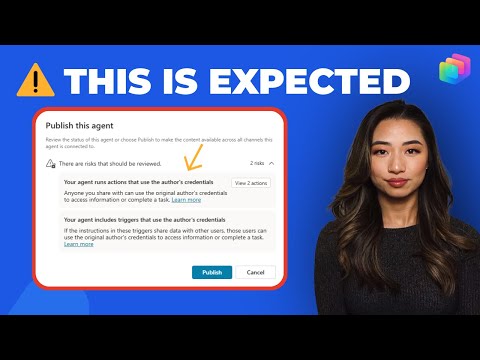
Copilot Studio: Connection Warning - Why
Power Platforms Consultant | Content Creator
Microsoft guide on Copilot Studio connection warning: maker credentials for knowledge, SharePoint risks, Purview audit
Key insights
- Copilot Studio connection warning: This warning is expected behavior, not a bug, when agent actions use authenticated services.
It appears to protect access by prompting re-authentication or signaling that a maker's credentials are in use. - knowledge sources: Documents added as Copilot knowledge sources always run under the maker’s credentials, so SharePoint file-level permissions are not enforced for those queries.
Design knowledge ingestion and sharing with that trust model in mind to avoid exposing restricted content. - tools and connectors: Tools (connectors) and agent flows behave differently from knowledge sources — by default they ask end users to sign in, which causes reconnection prompts during demos or token expiry.
Use maker-provided credentials for tools when you need stable, predictable behavior in production. - maker-provided credentials: Configure tools to use a maker’s or service account and set agent flows as run-only users to prevent repeated sign-ins.
Choose service accounts for centralized, auditable runs and end-user connections when actions must enforce each user’s own permissions. - Microsoft Purview: Copilot actions can be logged and audited through Microsoft Purview and runtime protections (like Defender webhooks) can block malicious or risky tool calls.
Plan logging and alerts so you can trace actions and meet compliance requirements. - publish vs redesign: Only publish a copilot when connections, permissions, and audit trails meet your governance and compliance needs.
If users gain unintended access or logging is insufficient, stop and redesign connection handling before broad deployment.
Video Summary and Context
In a recent YouTube video, author Isabel Liu explains why the Copilot Studio connection warning is expected behavior rather than a software bug. She walks viewers through how connections work when agents use knowledge sources, SharePoint, Power Automate, and other connectors in enterprise settings. As a result, the video emphasizes that misunderstanding this message can create real security, governance, and compliance risks.
Moreover, Liu frames the warning as a deliberate design choice tied to how credentials are handled at runtime. She outlines scenarios where makers see a notification that an agent uses the maker’s credentials, and she clarifies when that state is correct. Consequently, the video targets teams deploying copilots beyond personal use, urging them to align configuration with enterprise policies.
How Copilot Studio Connections Work
The video explains that by default, tools and agent flows call services using the end user’s authentication, which triggers reconnection prompts when tokens expire or change. However, makers can switch to maker-provided credentials so that agents run with a single, stable connection tied to the creator. This change stops frequent prompts and makes demos and production runs smoother while keeping a single audit trail for actions initiated by the agent.
Liu also differentiates between knowledge sources and connectors. Knowledge sources such as documents added into Copilot’s knowledge base always rely on the maker’s identity for retrieval, and SharePoint file permissions are not enforced in the same way as interactive connectors. Therefore, teams must understand that adding documents into knowledge stores can expose content beyond individual end-user permissions unless governance controls are in place.
Security, Logging, and Compliance Considerations
The video stresses that this behavior is by design to balance access with auditable control, not a defect to fix. Liu covers how actions are recorded in services like Microsoft Purview, and she explains what gets logged when Copilot interacts with corporate data. Consequently, IT teams can track agent actions, but they should verify whether logs meet regulatory or internal audit needs before broad deployment.
Importantly, Liu highlights runtime protection mechanisms such as real-time scanning that can block risky tool calls or prompt injection attempts. These safeguards help prevent data leakage or fraud, for example by stopping unauthorized bookings or sensitive data exfiltration. Still, defenders must tune alerts and design workflows so that security checks do not create unmanageable false positives during normal operations.
Tradeoffs: Usability Versus Least Privilege
The video outlines clear tradeoffs between user experience and strict least-privilege models. On one hand, using the maker’s credentials or service accounts reduces friction and avoids repeated sign-ins, which improves reliability for end users and demos. On the other hand, this approach concentrates access under a single identity, which can conflict with the principle of least privilege and increase risk if that identity is compromised.
Therefore, Liu advises teams to weigh productivity gains against potential exposure and to choose connections that fit their risk appetite. For instance, service accounts simplify operations but require stronger monitoring and rotation policies, while end-user connections preserve individual accountability but can create frequent authentication prompts that slow workflows. Balancing these options demands clear governance and tested processes for incident response.
Practical Guidance: Design, Auditability, and When to Pause
Finally, the presenter offers practical steps for designing connections that support auditability and compliance. She recommends configuring run-only accounts for Power Automate flows, documenting which tools use maker credentials, and validating Purview logs to ensure they capture required evidence. As a result, teams can demonstrate who accessed what and when, which helps during audits or investigations.
Liu also warns that publishing a copilot should not be automatic whenever warnings appear; sometimes the correct response is to stop and redesign the connection model. In particular, large-scale deployments require testing across tenant settings, careful selection between service accounts and end-user auth, and reviews of SharePoint knowledge sources so that sensitive content is not inadvertently exposed. Ultimately, her video offers a practical, security-minded roadmap for moving from prototypes to governed production deployments.
Keywords
Copilot Studio connection warning, Copilot Studio connection explained, Copilot Studio troubleshooting, fix Copilot Studio connection, Copilot warning not a bug, Microsoft Copilot Studio error, Copilot Studio connectivity issue, Copilot Studio debugging tips