- All of Microsoft
Microsoft Cybersecurity: 20-Year Lessons
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Microsoft expert demystifies Zero Trust with leadership analogies and practical Entra ID and Azure guidance
Key insights
- Zero Trust reframes security: treat every access request as untrusted and verify each one explicitly. Nicolas Blank uses simple analogies (locking a car, protecting a newborn) to help leaders grasp the approach quickly.
- Least Privilege means give users and systems only the access they need and nothing more. Applying least privilege reduces chances for attackers to move laterally after a breach.
- Assume Breach shifts focus from perfect prevention to rapid detection and response. Teams should design controls to limit damage and speed recovery when intrusions occur.
- Immune System Approach layers defenses across identity, endpoints, and continuous monitoring to catch threats early. This model emphasizes redundancy and fast containment, like a biological immune system.
- 96% Reduction highlights impact: enforcing phishing-resistant multi-factor authentication and strict identity controls can reduce breach risk by about 96%. Use this evidence to prioritize identity protection as a high-impact investment.
- Practical Starting Tools include identity hardening (MFA, conditional access), endpoint patching, and the Zero Trust Adoption Framework to deliver quick wins. Present clear, measurable steps to gain leadership support and show short-term benefits.
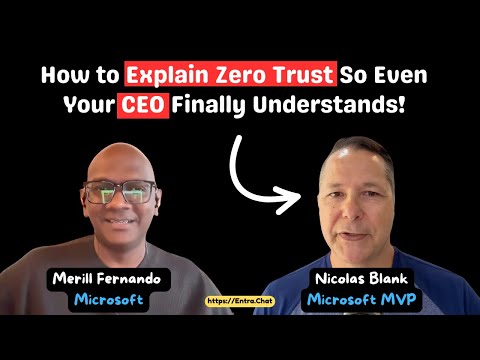
Merill Fernando's recent YouTube episode features a focused conversation with Nicolas Blank, a 20-year Microsoft MVP and founder of NBConsult, who breaks down complex security ideas into clear, practical advice. The video reframes common dialogues about Zero Trust by starting with everyday analogies, such as locking a car or protecting a newborn, to make the principles relatable for executives and technical leaders. As a result, viewers can quickly grasp why identity, continuous verification, and minimal access matter in modern environments. This article summarizes the key points and practical takeaways for teams planning Zero Trust journeys in 2026.
Zero Trust Made Simple
Blank opens by arguing that many conversations fail because they begin with technology rather than outcomes. Instead, he uses the baby analogy to explain least privilege: just as you limit who can handle an infant to reduce risk, you should limit user and system access to lower attack surface. This approach reframes security as a set of decisions about trust and exposure rather than a collection of tools. Consequently, leaders find it easier to approve changes when they understand the real-world logic behind them.
Continuing this thread, Blank emphasizes the need to assume breach and design defenses that reduce attacker payoff. He promotes an “immune system” model where layered controls detect and contain threats early, much like biological defenses slow and isolate infections. This mindset shifts investment from trying to block every possible attack to minimizing damage and recovery time. In turn, organizations can focus on measurable improvements such as faster detection and tighter isolation of compromised accounts.
Practical Steps and Tools
Blank highlights concrete starting points that teams can deploy quickly to gain traction. For example, prioritizing phishing-resistant multi-factor authentication for both users and machines, enforcing conditional access, and hardening endpoint configuration provide immediate reductions in risk. He stresses practical wins that deliver visible security gains without long, costly projects. These early successes often create momentum and help secure further funding for broader programs.
Moreover, he points to the Zero Trust Adoption Framework as a practical roadmap that begins with identity and progresses through endpoints, network segmentation, and monitoring. Blank lists tools and tactics to implement each phase and recommends starting where you can measure impact. By combining short-term wins with a long-term plan, teams balance action with strategic direction. This helps avoid the trap of deploying technology without operational change.
Tradeoffs and Challenges
While the benefits of a principles-first approach are compelling, Blank is candid about tradeoffs that organizations face. Rolling out strict controls like pervasive MFA and strict device compliance can cause friction with users and disrupt legacy workflows, which may slow adoption and require more support resources. Therefore, teams must weigh security gains against usability and business continuity, and implement changes incrementally to reduce resistance. This measured approach often requires clear communication, training, and temporary exceptions for critical operations.
Another challenge is balancing automation with human oversight in detection and response. Automation can improve speed and scale, but over-reliance may produce false positives or mask nuanced attacks that need human judgment. Conversely, manual processes strain small security teams and delay containment. Blank recommends a hybrid model where automation handles routine signals while skilled analysts focus on complex incidents, thus improving overall efficiency and effectiveness.
Measuring Impact and Reducing Attacker ROI
Blank stresses that success must be measured by reduced attacker return on investment rather than perfect prevention. He cites a repeated industry statistic that strong identity and endpoint controls can reduce the likelihood of compromise dramatically. Consequently, teams should track metrics like time to detect, time to contain, and the percentage of accounts protected by phishing-resistant authentication. These metrics make the business case clearer and align security goals with organizational risk appetite.
Furthermore, the guest explains how isolating tenants, improving supply chain security, and accelerating vulnerability remediation each lower the rewards for attackers. By making intrusions costlier and less predictable, organizations can shift the economics of attack and deter many adversaries. This strategy also complements long-term initiatives such as secure development practices and continuous monitoring, which together create a more resilient environment.
Getting Leadership Buy-In
Finally, Blank details how to engage executives and boards by using relatable analogies and clear metrics. He recommends demonstrating short-term wins, quantifying risk reduction, and aligning security measures with business goals to gain sustained support. With clear storytelling and measurable outcomes, leaders are more likely to fund broader Zero Trust work and accept temporary operational changes. As a result, security teams can move from emergency fixes to strategic programs that scale over time.
In sum, the YouTube conversation hosted by Merill Fernando provides a concise, practical playbook for organizations adopting Zero Trust in 2026. By starting with principles, focusing on measurable wins, and balancing tradeoffs between usability and protection, teams can build resilient defenses that reduce attacker incentives and support business goals. For security teams and leaders, the episode offers both a mindset shift and actionable steps to make progress without getting lost in tool choices.
Keywords
cybersecurity first principles, Microsoft MVP cybersecurity lessons, cybersecurity best practices, enterprise cybersecurity strategy, security fundamentals for IT, practical cybersecurity tips, long-term cybersecurity lessons, Microsoft MVP security insights