- All of Microsoft
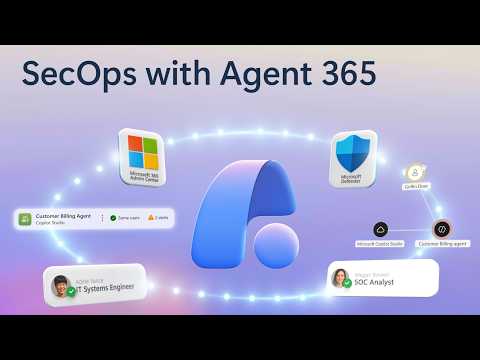
Agent 365: Streamline Defender Ops
Software Development Redmond, Washington
Protect AI agents with Microsoft Defender, Entra and Copilot Studio for unified visibility, blocking and automated remediation
Key insights
- Agent 365: The Microsoft video shows Agent 365 as a control plane that makes AI agents visible, governable, and defendable across your tenant.
It surfaces agent inventory and centralizes governance so teams can treat agents like standard IT assets. - Microsoft Defender: Defender integrates agent telemetry into the same investigation and incident workflows SOC teams already use.
Analysts can pivot from IT alerts into the full incident graph for deeper investigation. - real-time protection: Defender can block malicious tool invocations and detect persistent jailbreak attempts at runtime.
This reduces attacker dwell time by stopping risky actions as they occur. - Microsoft Entra: The demo shows automated response by linking incidents to Entra conditional access to revoke sessions and force password resets.
This lets teams quickly cut off compromised identities tied to malicious agents. - Advanced Hunting: Agent 365 provides observability data that you can query with KQL using built-in hunting templates.
Teams can find overpermissioned or risky agents and pull unsafe builds from the Agent Registry. - managed enterprise assets: The model assigns clear admin roles (Defender, Entra, Purview, Microsoft 365) so agents get inventory, policy controls, and data governance.
This gives IT and SOC a shared way to reduce exposure and prevent future incidents.
Microsoft video overview
The video titled Agent 365 | Security Operations in Defender was published by Microsoft and features Spencer Berg, AI & Security Product Manager, explaining new tools for managing AI agents. The piece demonstrates how the company combines visibility, threat detection, and remediation workflows across Microsoft security products. Consequently, it positions Agent 365 as a control plane that surfaces agent activity into existing security operations. Overall, the segment aims to show how IT and SOC teams can work together to manage agent risk without adding a separate security product.
What Agent 365 promises
First, the video frames Agent 365 as a way to discover and inventory AI agents across a tenant so teams can see who or what is acting on behalf of automation. In addition, the system links agent activity into Microsoft Defender for detection and investigation, and into the Microsoft 365 admin center for IT-focused triage. This integrated view is designed to let administrators pivot from an IT alert into a full SOC incident graph with minimal friction. Furthermore, the demo highlights the ability to trace suspicious outcomes back to the agent and the user or credential that invoked it.
How Defender, Entra and admin tools integrate
Next, the video explains how Defender, Microsoft Entra, Purview, and the Microsoft 365 admin center share responsibilities for securing agents and their data. For example, Defender handles detection and runtime blocking, while Entra enforces identity and access policies and can revoke sessions when an agent appears compromised. Moreover, admins can trigger a conditional access policy from the incident so a user session is revoked and a password reset is forced quickly. Thus, the workflow aims to enable coordinated remediation across security and IT teams using familiar consoles.
Real-time protection and hunting
Importantly, the video showcases real-time protections such as scripting or tool-blocking when an agent attempts risky actions and jailbreak detection for agents developed in Copilot Studio. Additionally, Defender exposes telemetry through the Microsoft 365 app connector and provides Advanced Hunting templates for agent-focused queries. These templates reportedly help identify overpermissioned agents and those using standing credentials to run malicious builds. Consequently, teams can both contain active threats and hunt for risky configurations before they become incidents.
Planned features and timelines
Microsoft states that starting in June 2026 Defender will add asset context mapping for agents, linking them to devices, servers, identities, and reachable resources so teams can assess blast radius more clearly. In addition, policy-based controls, runtime blocking and alerts via Intune and Defender are scheduled for public preview around the same time. Therefore, organizations should expect expanded visibility and enforcement tools in the near term, which may change how they inventory and manage agent lifecycles. These changes promise tighter control but will also demand updated internal processes and training.
Tradeoffs and operational challenges
While the video emphasizes centralized control, it also implies tradeoffs between visibility and complexity; adding agent telemetry improves detection but increases data volume and analyst workload. Moreover, integrating agent governance across Defender, Entra, Purview, and Microsoft 365 requires coordination among security, identity, compliance, and IT teams, which can slow adoption. False positives and noisy alerts represent a second challenge, because overly aggressive blocking can interrupt legitimate automation and developer workflows. Thus, organizations must balance protection with operational continuity by tuning rules and defining clear escalation paths.
Security risks and attacker behavior
The demonstration notes that attackers may try jailbreaks, persistent agent execution, or credential misuse, and that Defender aims to surface patterns tied to these behaviors. However, attackers will adapt, and runtime blocking is not a one-time fix; defenders must maintain detection logic and response playbooks. Additionally, mapping agent identity to human operators or service accounts can be difficult when agents run across cloud and on-prem systems. Consequently, effective defense requires both technical controls and governance practices that include least-privilege design and regular audits.
Practical implications for IT and SOC teams
Practically speaking, the video asks IT and SOC teams to treat agents as managed assets that require the same lifecycle controls as applications and devices. Therefore, organizations should plan for new inventory processes, role definitions, and policy templates so agents do not become blind spots. At the same time, teams must avoid heavy-handed policies that disrupt legitimate automation, and they should apply staged rollouts to validate detection tuning. In short, successful deployment will depend on cross-team collaboration, clear ownership, and iterative tuning.
Conclusion
In summary, the Microsoft video presents Agent 365 as a step toward making AI agents observable and governable within existing Defender workflows, with coordinated remediation through Microsoft Entra and admin tools. While the proposed features offer stronger visibility and faster incident response, they also introduce operational complexity and the need for careful tuning to avoid disrupting business automation. Ultimately, the initiative reflects a broader shift to manage AI agents as first-class enterprise assets, but organizations should prepare for both the benefits and the work required to realize them.
Keywords
Microsoft 365 Defender, Security operations, Defender for Endpoint, Incident response, Threat hunting, XDR, SOAR automation, Endpoint detection and response