- All of Microsoft
Maester 2.2: Active Directory Audit Tips
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Microsoft expert: Maester Active Directory security testing with PowerShell, Windows Server, Entra ID, Intune and GPOs
Key insights
- Maester 2.2 adds a major on‑prem Active Directory test suite: 269 opt-in Active Directory checks across 19 areas (users, groups, computers, service principal names, password and fine‑grained policies, replication, DNS, trusts, schema, GPO inventory and state, and DACL/privileged access analysis).
- AD testing is explicitly opt-in. Use Connect-Maester -Service ActiveDirectory to enable AD checks; the default flow will not touch domain controllers. Do not run scans on a domain controller. Maester is report-driven so results are for review and remediation, not just pass/fail.
- Permissions: many checks need read-only access and a plain domain user suffices for common scans; a full run that inspects tier‑zero artifacts requires higher privileged accounts. Run AD tests with commands like Invoke-Maester -Path "./ad" -SkipGraphConnect -NonInteractive or targeted paths such as "./ad/user".
- Scope and role: Maester extends hybrid coverage to assess both on-prem and cloud identity from one framework. It complements tools like PingCastle, Purple Knight, and Locksmith by focusing on automated, evidence-backed reporting and drift detection rather than configuration changes.
- Operational notes: expect large-forest performance limits—teams reported long, memory‑heavy runs (an 18‑hour out‑of‑memory scenario). Split big assessments with tags and merge results to manage scale; Maester tags help track anti‑patterns over time.
- Road map highlights: planned moves include replacing the ActiveDirectory PowerShell module with LDAP and .NET calls, adding multi-platform support, alternate credentials and gMSAs, multi-domain aggregation and focused tiering tests to better validate ESAE and enterprise access models.
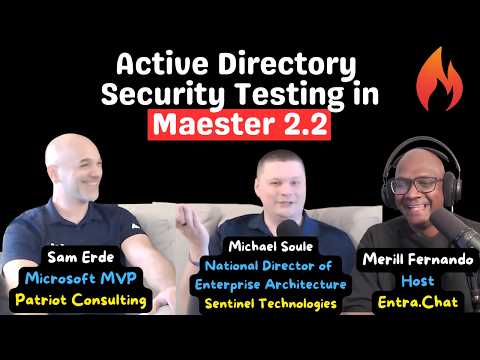
Merill Fernando’s recent YouTube episode at HIP Conf examined the new Active Directory capabilities in the open-source PowerShell testing framework Maester. The episode features co-maintainers Mike Soule and Sam Erde, who explain how Maester 2.2 adds a significant set of opt-in checks for on-premises environments. The discussion clarifies the intent, the safety choices, and practical uses for hybrid identity assessments.
What Maester 2.2 Adds
According to the video, Maester 2.2 introduces an extensive Active Directory test suite that covers hundreds of checks across many areas of a directory. The release explicitly treats AD testing as opt-in, which means the default connection flow will not contact domain controllers unless administrators request it. Consequently, this design reduces accidental disruption while still enabling deep coverage when needed.
The suite inspects users, groups, computers, service principal names, GPO state, DACLs, DNS, replication, and schema among other areas. Moreover, the maintainers emphasize that tests are report-driven: results are meant to guide investigation and remediation rather than act as binary pass/fail stamps. Therefore, teams can use findings to prioritize work while documenting evidence for future audits.
A companion point in the episode highlights that some checks are labeled "investigate and monitor" rather than simple fails because context matters for directory health. Tags can track anti-patterns over time so that long-term trends become visible without creating noise from transient states. Thus, the framework helps balance signal and noise in large estate assessments.
Running the Tests and Permissions
Fernando and the guests walk viewers through the explicit connection model, explaining commands such as Connect-Maester -Service ActiveDirectory and targeted runs via Invoke-Maester. Running AD tests does not require elevated rights for many checks; read-only access is sufficient for most inventory and configuration scans. However, a fuller run that analyzes privileged access or DACLs may need higher privileges or tier-zero credentials.
The show stresses a strong safety warning: never run the full scan directly on a domain controller, and avoid scanning with overly broad credentials. In addition, the team recounts a real-world memory exhaustion example to illustrate that very large forests can strain a scan if not split. Consequently, the framework supports splitting assessments by tag and merging results later to reduce runtime and memory pressure.
Another practical takeaway is that Maester’s opt-in AD support preserves operational safety while enabling repeatable, auditable checks. The report-driven outputs are designed to feed remediation workflows instead of forcing immediate changes. Therefore, organizations can adopt the tool incrementally and validate fixes over time without disruptive single-shot operations.
Tradeoffs and Technical Challenges
The episode outlines several tradeoffs administrators face when testing on-prem directories. For instance, deep access control analysis yields valuable findings but can require higher privileges and careful scoping to avoid exposing sensitive details. At the same time, restricting tests to lower privileges reduces risk but can miss complex privilege escalation paths.
Performance and scale present another set of tradeoffs. Maester can validate very large forests, but doing so in one pass may cause high memory use and long runtimes. Therefore, teams must decide between comprehensive single-run reports and staggered, tag-based scans that reduce load but require careful result merging.
A final challenge lies in interpreting operational health items versus security findings, since some checks are primarily about stability rather than attack surface. The maintainers recommend treating these categories differently in remediation plans so that security teams focus on privilege and access risks while operations teams address reliability. This separation helps prioritize scarce resources effectively.
How Maester Fits with Other Tools
Fernando and his guests position Maester alongside other tooling like PingCastle, Purple Knight, and Locksmith while clarifying differences in approach. Unlike configuration tools such as DSC, Ansible, or Terraform, Maester reports state with evidence rather than enforcing changes. Consequently, Maester is best suited for assessment and validation workflows, not configuration management.
The episode also covers how Maester complements cloud-focused checks for Microsoft 365 and Entra, enabling a unified testing workflow for hybrid environments. By consolidating results into coherent reports, teams gain a clearer picture of identity risk across both on-prem and cloud systems. Thus, organizations can align hybrid security efforts without juggling multiple disconnected reports.
Looking ahead, the maintainers discuss replacing the ActiveDirectory PowerShell module with LDAP and .NET approaches, expanding multi-platform support, handling alternate credentials and gMSAs, and improving multi-domain aggregation. These plans suggest a steady push to make the framework more flexible while keeping operational safety and evidence-based reporting central to the product.
Practical Guidance and Next Steps
For teams interested in trying Maester’s AD checks, the video advises starting with read-only runs and targeted paths to limit scope and understand results. Then, use tags to break up larger assessments and merge reports for a complete view. This phased approach reduces risk while proving value to stakeholders.
Finally, Fernando’s conversation with the maintainers reinforces that Active Directory is far from dead; instead, it remains a critical plane to secure in hybrid estates. By combining careful permission choices, staged scans, and report-driven remediation, organizations can balance depth and safety while improving directory security over time.
Keywords
Active Directory security, AD security testing, Maester 2.2 security testing, Active Directory penetration testing, Maester 2.2 tutorial, Maester AD assessment, AD audit tools, Active Directory hardening