- All of Microsoft
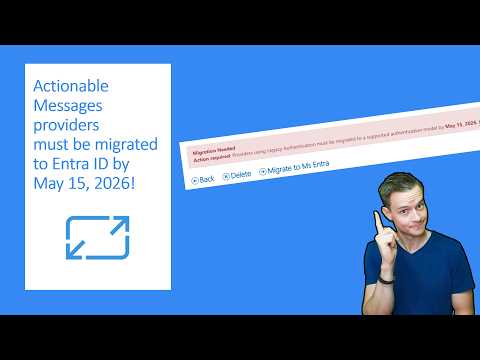
Entra ID: Migrate Actionable Messages
Power Platform expert, Business Applications MVP, international speaker.
Migrate Outlook Actionable Messages to Entra ID with expert steps, scenario selection and Power Automate guidance
Key insights
- Deadline: Migrate all Actionable Messages providers from External Access Tokens to Microsoft Entra ID by May 15, 2026 to avoid failures; new EAT registrations have been blocked since November 21, 2025.
- What to migrate: Any provider that used EAT must be re-created or migrated to use Entra ID tokens, since these tokens provide OAuth-based, JWT authentication for in-email actions.
- Migration workflow: Open the Actionable Messages Developer Dashboard, choose to migrate an existing provider or register a new one, then link it to an Entra app and refresh the provider status to get approval.
- App registration: In Microsoft Entra register a new app, record the Application (client) ID and App ID URI, expose an API scope, and grant admin consent for your tenant before configuring the provider.
- Backend validation: Update your service to verify the Provider-Id header and decode the JWT in the Action-Authorization header, checking the appid claim against your client ID; then run end-to-end tests to confirm tokens are accepted.
- Integration notes: Select the "Power Automate scenario" only when the provider is used by Power Automate; choose "Not a Power Automate scenario" if other services will call the provider, update platform-specific settings (for example ServiceNow properties), and test flows to prevent downtime.
Introduction
In a recent YouTube video, Tomasz Poszytek [MVP] walks viewers through migrating Actionable Messages providers from legacy external access tokens to Microsoft Entra ID authentication. The video explains why this migration matters, demonstrates the steps in the developer dashboard, and highlights testing steps to confirm a successful cutover. Given a retirement deadline for the legacy approach, Tomasz emphasizes the need to act promptly to avoid service disruption. Consequently, administrators and developers should plan the migration carefully and validate their integrations before enforcement.
What the Video Covers
Tomasz organizes the tutorial into clear chapters that begin with an overview and then show the actual migration, scenario selection, provider settings, approval, and testing. He notes that selecting the correct scenario matters: the default Power Automate scenario should be used for flows running in Power Automate, while the alternative Not a Power Automate scenario applies when other services consume the provider. Furthermore, Tomasz demonstrates how provider status moves to Approved after entering the new Entra application identifiers and refreshing the dashboard. Thus, the video is practical for teams that need a direct, step-by-step approach rather than a conceptual discussion.
Step-by-Step Migration Walkthrough
First, the video shows signing into the Actionable Messages developer dashboard and choosing an existing provider to migrate or registering a new one with Microsoft Entra ID. Next, Tomasz guides viewers through creating an app registration in the Entra admin center, copying the Application (client) ID and the auto-generated App ID URI, and exposing an API scope so the provider can request the correct token. After app registration, he explains entering the Entra Application ID and App ID URI into the dashboard, watching the provider transition to an approved state, and performing a refresh to confirm the change.
Then, Tomasz turns to backend validation, showing how to decode the JWT received in the Action-Authorization header and verify the appid claim against the new client ID. He describes checking the Provider-Id header to ensure the originator matches the registered provider and suggests common checks that resolve 401 errors, such as verifying scopes and admin consent. For integrations like Power Automate and ServiceNow, Tomasz points out small but crucial differences, for example updating ServiceNow properties to reference the new Provider ID and confirming the originator in Power Automate triggers. Overall, the walkthrough balances configuration, validation, and testing in a single flow to reduce surprises after migration.
Key Technical Considerations
Migrating involves not only changing tokens but also updating how your service validates requests and enforces scopes, so developers should expect code changes in token validation logic. In particular, verifying the JWT signature, confirming the appid claim, and ensuring the Provider-Id header match are essential steps that replace the simpler checks used with external access tokens. Moreover, exposing an API with an appropriate scope and granting admin consent are administrative tasks that require tenant-level privileges and coordination with identity owners. Therefore, teams must plan for both developer work and administrative approvals to complete the migration smoothly.
Security improves with Entra ID because tokens are standard OAuth 2.0 JWTs that include verifiable claims, but that improvement comes with tradeoffs such as additional configuration complexity and the need to manage app registrations over time. Also, multi-tenant or cross-organization scenarios can complicate consent and token issuance, which means organizations should validate tokens from their expected issuer and ensure their app registration settings match their operational model. Consequently, testing across environments and documenting the updated validation flow reduces the risk of blocked or failing actionable messages in production.
Tradeoffs and Challenges
One tradeoff is between security and administrative overhead: adopting Microsoft Entra ID strengthens identity guarantees, yet it requires extra steps like exposing APIs, creating scopes, and granting admin consent. This administrative work can introduce delays, particularly in larger organizations where tenant-level approvals follow formal change control processes. On the other hand, sticking to legacy methods is not viable due to the retirement deadline, so teams must accept short-term overhead for longer-term benefits.
Operational challenges also include timing the migration to avoid disruption, handling unexpected 401 errors during rollout, and coordinating with third-party services that consume actionable messages. For example, ServiceNow users need to update a specific property to the new Provider ID, and Power Automate flows must align with the selected scenario; otherwise, messages may be rejected. Thus, a staged approach with thorough testing and rollback plans mitigates risk while ensuring continuity of service.
Testing, Recommendations, and Wrap-up
Tomasz concludes by encouraging teams to test migrated providers end to end, including token validation, header checks, and the actual adaptive card actions in Outlook. He recommends a careful review of scopes, confirming that the originator matches the expected provider, and running a subset of traffic through the migrated provider before switching all users over. Additionally, documenting the new process and updating operational runbooks helps support teams respond quickly if issues arise after migration begins.
In summary, the video by Tomasz Poszytek [MVP] provides a concise, usable guide to move Actionable Messages providers to Microsoft Entra ID, balancing practical steps with warnings about common pitfalls. While the migration demands planning and administrative work, it delivers stronger authentication and compatibility with modern identity standards, making it a necessary upgrade for teams that rely on actionable messages in Outlook.
Keywords
Migrate Actionable Messages to Entra ID, Entra ID Actionable Messages migration, Actionable Messages provider Entra ID, Entra ID authentication for Actionable Messages, Outlook Actionable Messages Entra ID, Microsoft Entra ID migration guide, Update Actionable Messages provider to Entra ID, Entra ID OAuth for Actionable Messages