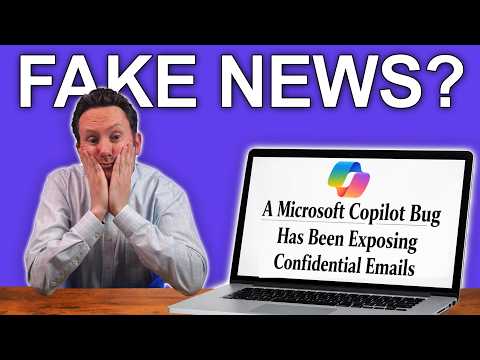
Microsoft 365 Copilot Security Exposed
Consultant at Bright Ideas Agency | Digital Transformation | Microsoft 365 | Modern Workplace
Microsoft Three Sixty Five Copilot DLP bug explained by expert: narrow exposure, Purview DLP, Copilot Chat fixes
Key insights
- DLP bug (CW1226324): The video explains a real but narrow code error that let some Copilot Chat sessions access confidential emails in specific setups.
Microsoft released a patch and the problem did not mean broad tenant-to-tenant data leakage. - Headlines vs. reality: Media coverage overstated the scope by saying Copilot was "exposing" all emails.
The incident affected particular DLP handling and configuration, not a wholesale collapse of Copilot security. - AI incidents context: The presenter compares this Copilot bug with other AI issues across the industry, including leaks and model vulnerabilities.
That context shows bugs and misconfigurations, not just one vendor, drive most AI data risks. - Defense-in-depth: Copilot relies on layered controls such as harmful-output filters, prompt-injection classifiers, and tenant isolation.
Integration with Microsoft Purview lets organizations apply DLP rules to AI interactions. - Admin actions: Review and tighten Purview DLP policies, audit permissions, check the Copilot admin tab, and apply all security updates.
Enforce least-privilege and monitor logs for unusual Copilot activity. - Practical takeaway: Don’t panic from sensational headlines.
Use layered controls, keep systems patched, and adopt the routine of test, monitor, and enforce policies for AI features.
Overview: Reassessing the Headlines
In a recent YouTube video, Nick DeCourcy of Bright Ideas Agency walks viewers through the true scope of the Microsoft 365 Copilot security incident labeled CW1226324. He argues that sensational headlines claiming Copilot was broadly "exposing confidential emails" missed important technical details, and therefore overstated the risk. Consequently, his analysis seeks to separate the narrow, concrete bug from the broader public narrative that followed. Overall, the video recommends calm, targeted responses rather than panic-driven reactions.
What Actually Happened
DeCourcy explains that the incident was a specific Data Loss Prevention issue affecting certain Copilot flows, not a wholesale breach of tenant isolation or mass exfiltration. The bug allowed some content to be included in Copilot processing in ways administrators might not have expected, yet it was not the same as openly publishing user mailboxes to external systems. Moreover, Microsoft’s remediation and advisories focused on the particular DLP rules and scenarios involved, which limited the exposure window.
Context: AI Security Across the Industry
Importantly, the video places the Copilot bug in a broader pattern of AI-related incidents across vendors, noting issues reported with other models and third-party chat apps. DeCourcy highlights that vulnerabilities—such as model jailbreaks, configuration errors, and third-party leaks—have appeared in many ecosystems, and that Copilot’s issue is one of several symptomatic problems as enterprises adopt AI at scale. Therefore, understanding Copilot requires seeing it alongside ChatGPT, Gemini, and independent chat platforms rather than treating it as a unique failure.
How Copilot’s Security Model Works
According to the analysis, Copilot is designed around tenant data use, layered safeguards, and integration with governance tools such as Purview and DLP policies. In practice, this means Copilot typically processes organizational data within Microsoft boundaries and applies classifiers to detect harmful prompts and sensitive content before model execution. However, the episode exposed limits in how those protections interact with specific DLP configurations and admin settings, which is why careful policy design matters.
Tradeoffs: Security, Usability, and Complexity
DeCourcy emphasizes tradeoffs organizations face when balancing security and usability: stricter DLP and prompt filtering reduce the chance of accidental disclosure but can also degrade the user experience and the usefulness of Copilot. Conversely, permissive settings improve productivity but raise risk, particularly when administrators underestimate how AI prompts surface data. In addition, the complexity of modern Microsoft 365 licensing and feature sets means that some protections are bundled while others require higher-tier plans, so teams must weigh cost, coverage, and operational overhead.
Challenges in Detection and Policy Enforcement
The video outlines specific challenges, such as reliably detecting prompt injection and balancing false positives against missed exposures. Automated classifiers are helpful, yet they can be evaded by clever inputs or by unanticipated interactions between services. Furthermore, administrator tools must scale: large tenants with many sites and apps need automated remediation and clear visibility, otherwise policy drift and over-permissioned identities create long-term risk.
Practical Recommendations for IT and Security Teams
DeCourcy recommends a layered response: review and tighten relevant DLP rules, validate Copilot governance settings in the admin center, and run controlled tests to confirm expected behavior. He also advises documenting use cases where Copilot is allowed to access tenant data and applying the principle of least privilege to connectors and app permissions. Finally, routine monitoring and incident playbooks help teams react quickly if a policy gap appears.
Why the Nuance Matters
Ultimately, the video argues that nuance shapes both public understanding and organizational response. Sensational coverage can divert attention from the practical steps needed to secure services and can erode trust without providing actionable guidance. By contrast, DeCourcy’s detailed walkthrough encourages decision-makers to focus on configuration, governance, and training—measures that reduce real risk while preserving the benefits of AI tools.
Bottom Line
Nick DeCourcy’s analysis supplies a measured perspective: the Microsoft 365 Copilot issue was real but narrow, and it highlights systemic challenges common to AI deployments rather than a unique, catastrophic failure. For IT leaders, the takeaway is clear—treat this as a governance and configuration problem to be managed through policies, tooling, and testing, while keeping an eye on evolving AI threats across the ecosystem. Consequently, thoughtful, proportionate action will better protect organizations than alarmist headlines.
Keywords
Microsoft 365 Copilot security, Copilot data privacy, Copilot compliance and governance, Copilot threat detection, M365 Copilot risk mitigation, Copilot enterprise security best practices, Copilot AI security concerns, Microsoft Copilot zero trust