Entra: Governance, PAM & Agent IDs
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Open-source Entra masterclass unlocks Entra ID governance, privileged access, lifecycle workflows and Agent ID labs
Key insights
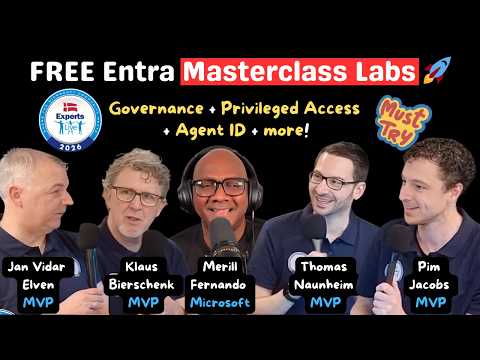
- Open-sourced labs from a YouTube masterclass that recorded a five-person podcast at Experts Live Denmark make full Microsoft Entra training freely available.
These labs reproduce the seven-hour workshop so teams can follow step-by-step exercises at their own pace. - Core topics covered include inbound provisioning, lifecycle workflows, Privileged Access Management, offboarding, backup & restore, and the new Agent ID concepts.
The materials show practical setups and patterns for each area. - Hands-on deployment benefits let teams replicate enterprise patterns in test tenants and reduce trial-and-error in production.
The labs include deployable exercises and blueprints to accelerate real-world implementation. - Security and governance focus on reducing risk: separate governance for admin accounts, phishing-resistant authentication (FIDO2/passkeys), protected actions to avoid accidental deletions, and automated lifecycle enforcement.
These controls help keep identities clean during onboarding and offboarding. - Agent ID and agent management introduce ways to govern AI and automation agents with blueprints and multi-tenant scenarios.
Early adoption helps prepare for agent scale and future Entra features. - Practical outcomes and community support include reusable logic apps, Access Package patterns, and guidance for linked identities and Cross-Tenant Sync.
Teams gain faster skill-building, stronger compliance, and repeatable governance from the shared lab content.
Overview of the Video and Open-Source Release
In a recently published YouTube video, Merill Fernando hosts a detailed session that documents a seven-hour masterclass on Microsoft identity and access topics, now made available as open-source labs. The session features a group of experts who walked through hands-on exercises and real-world scenarios, and the video aims to let practitioners reproduce those patterns in their own environments. As a result, the release promises practical guidance for teams working with Entra and related identity technologies, and it invites the community to learn from the same lab materials used during the live event.
What the Open-Source Labs Contain
The labs cover a wide scope, beginning with Entra ID inbound provisioning and moving through lifecycle workflows, governance, and privileged access controls. Moreover, the materials document techniques for backup and restore, protected actions to prevent accidental deletions, and automated offboarding that removes residual access when employees leave. The release also introduces blueprints and hands-on examples for dealing with linked identities and cross-tenant scenarios, which teams often face when integrating external identity sources or managing partners.
In addition to traditional identity topics, the masterclass demonstrates how to secure privileged admin accounts with phishing-resistant methods and separate governance paths, and it shows ways to combine Access Packages and Logic Apps for automated governance. These exercises aim to balance configurability with operational safety, giving administrators templates they can adapt rather than rigid scripts they must follow verbatim. The lab materials are available to download from the project repository, enabling repeatable practice and faster on-boarding for engineers and security teams.
Security and Governance Tradeoffs
Adopting the lab patterns offers clear security benefits, yet teams must weigh tradeoffs between automation, control, and complexity. For example, automating lifecycle workflows reduces human error and speeds provisioning, but it also increases reliance on well-tested automation logic; a misconfigured workflow could inadvertently assign the wrong access or skip crucial checks. Therefore, the labs stress testing and staged deployment to catch issues early, which adds time to implementation but reduces long-term risk.
Similarly, enforcing strict privileged access policies improves resilience against compromise but can hinder productivity if approvals or elevation steps are too burdensome. Consequently, the material recommends a measured approach: implement stronger controls for highly sensitive roles while providing streamlined paths for lower-risk tasks. This balance requires ongoing review, and teams should monitor both security signals and operational feedback to adjust policies without creating unnecessary friction.
Agent ID and Future-Proofing Identity Workflows
One of the session highlights is an early look at Agent ID and example blueprints for managing agents that act on behalf of users or systems. As organizations adopt AI-driven automation and distributed services, the number of non-human identities grows, and the labs tackle how to govern those identities with lifecycle controls and least-privilege models. This forward-looking content helps engineers anticipate challenges such as credential sprawl, delegated permissions for agents, and the need to track agent behavior for audit and compliance.
However, introducing agent management also raises practical challenges: teams must decide how to separate agent privileges from user privileges, how to rotate secrets or keys safely, and how to instrument monitoring so anomalous agent activity triggers useful alerts. The masterclass materials explore these tradeoffs and propose patterns that favor observable, short-lived credentials combined with clear ownership and automated reclamation when agents are no longer needed. Adopting those practices will require organizational alignment and investment in tooling, but they reduce long-term operational risk.
Practical Adoption, Community Support, and Challenges
For teams ready to adopt the labs, the video outlines a sensible rollout path that starts with sandbox deployments and ends with staged production migrations. Moreover, the authors recommend pairing engineers with business owners to ensure access models reflect real needs, and to avoid over-permissioning that often follows rushed rollouts. The materials encourage testing backup and restore procedures, exercising offboarding workflows, and validating protected actions in controlled environments before wide release.
Finally, while the open-source release lowers the barrier to learn and deploy advanced identity patterns, success still requires time, discipline, and cross-team collaboration. Organizations must balance the speed of automation with careful policy design, and they must invest in monitoring and incident response to address mistakes or misuse quickly. In short, the masterclass provides practical blueprints and examples, but teams should expect to adapt them to their unique environments while paying attention to the tradeoffs between security, usability, and operational overhead.
Keywords
Microsoft Entra masterclass, Entra governance tutorial, Privileged Access Management Entra, Agent ID lab Entra, Open-source Entra lab, Entra identity governance, Azure AD Entra tutorial, Entra privileged access best practices