Microsoft Zero Trust Errors That 90% of Firms Overlook
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Zero Trust, Compliance, Conditional Access, AI, Excel, Intune, ADFS, Zero Trust Workshop
Key insights
- Zero Trust as an evolving strategy: Most companies make the mistake of treating Zero Trust as a one-time project. The right approach is to see it as a continuous process that adapts to changes in cloud, hybrid work, and technology environments.
- Identity and device verification: Microsoft’s model requires strong identity checks using multifactor authentication (MFA), biometrics, and strict device health validation before access is granted. This helps remove any implicit trust for users or devices inside or outside the network.
- Least privilege access and segmentation: Organizations should give users and devices only the minimum access they need. Proper network segmentation prevents attackers from moving freely if they gain entry.
- Pervasive telemetry and auditing: Continuous monitoring with detailed telemetry, auditing, and validation of security controls is essential to keep up with new risks and maintain a strong Zero Trust posture.
- Extending Zero Trust everywhere: Microsoft recommends applying Zero Trust principles across all digital assets—not just identities but also endpoints, applications, networks, and multi-cloud setups. Tools like Microsoft Entra, Intune, Purview, and Defender help support this broad coverage.
- Main pitfalls to avoid: Common mistakes include treating Zero Trust as finished after setup, ignoring new cloud integrations, not enforcing device health or phishing-resistant authentication, giving too much access, and skipping network segmentation.
Introduction: Revealing the Zero Trust Security Gaps
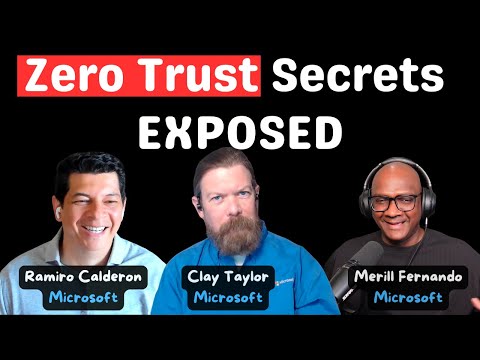
In a recent YouTube video, Merill Fernando sits down with Microsoft insiders Clay and Ramiro to discuss the most common mistakes enterprises make when adopting Zero Trust security. Drawing from their extensive experience running over 150 Zero Trust workshops globally, the two Customer Experience (CxE) architects reveal why even well-funded organizations are still falling short in their security efforts. This conversation uncovers not only the core errors but also the critical tradeoffs and evolving challenges that businesses face as they strive to secure their environments.
As the Zero Trust approach becomes more widely adopted, understanding its nuances and common pitfalls is essential for organizations looking to strengthen their security posture in today’s fast-changing digital landscape.
The Evolving Nature of Zero Trust
One of the main insights highlighted in the discussion is that many organizations mistakenly treat Zero Trust as a one-time project rather than an ongoing, adaptive strategy. Clay and Ramiro point out that environments, devices, and identities are constantly changing—especially with the rapid adoption of cloud services and hybrid work models. As a result, security must also be continuously monitored and adjusted.
The Microsoft experts emphasize that failing to adapt Zero Trust controls leaves gaps that attackers can exploit. For instance, a company may deploy new SaaS applications or APIs without updating their security rules, inadvertently creating new vulnerabilities. Therefore, ongoing vigilance is critical to maintain a secure environment.
Key Pillars: Identity, Device Verification, and Least Privilege
A cornerstone of Microsoft’s Zero Trust philosophy is robust identity and device verification. The video underscores the importance of using phishing-resistant multifactor authentication (MFA) and biometric checks to confirm user identities. Additionally, verifying the health and compliance of every device before granting access is crucial.
Furthermore, the principle of least privilege access is discussed at length. Clay and Ramiro explain that organizations must limit both users and devices to only the resources they truly need. Broad network access or unsegmented VPNs can allow attackers to move laterally within an organization if a single account is compromised, highlighting the need for granular segmentation.
Continuous Monitoring and Telemetry
The conversation also brings attention to the necessity of comprehensive monitoring and auditing. According to the Microsoft team, maintaining a strong Zero Trust posture requires constant validation of security controls and real-time detection of suspicious activity. This approach enables organizations to respond quickly as threats evolve, rather than relying on static, outdated rules.
By leveraging telemetry and automated auditing, companies can identify potential gaps and ensure that their Zero Trust framework remains effective even as the technology landscape shifts.
Extending Zero Trust Across the Digital Estate
Another key takeaway from the video is the need to apply Zero Trust principles beyond just user identities. Microsoft encourages organizations to extend these strategies to endpoints, applications, networks, and even across multicloud environments. Their integrated security tools—such as Microsoft Entra for identity, Intune for device compliance, and Defender for threat protection—help organizations build a holistic defense.
However, the experts note that achieving this broad coverage comes with challenges. Companies must balance the complexity of managing multiple platforms with the need for unified security policies, which can require specialized training and ongoing effort.
Common Pitfalls and the Road Ahead
The video identifies several frequent mistakes, such as treating Zero Trust as a completed task, overlooking the growing complexity of cloud and SaaS integrations, and neglecting device health checks or strong authentication. These missteps can undermine even the most well-intentioned security programs.
Looking forward, Clay and Ramiro predict that artificial intelligence will play an increasing role in automating and enhancing Zero Trust strategies. Nonetheless, they caution that human oversight and continuous improvement remain vital. The experts advise organizations to view Zero Trust as a dynamic journey, requiring persistent attention and adaptation to stay ahead of emerging threats.
In summary, the insights from this YouTube discussion highlight that the true strength of Zero Trust lies in its continuous evolution and comprehensive application. Organizations that embrace this mindset—and avoid the temptation to treat security as a one-time fix—will be better positioned to protect their digital assets in the years to come.
Keywords
Zero Trust mistakes Zero Trust security Microsoft Zero Trust insider tips cybersecurity errors corporate security flaws network protection failures data breach prevention strategies