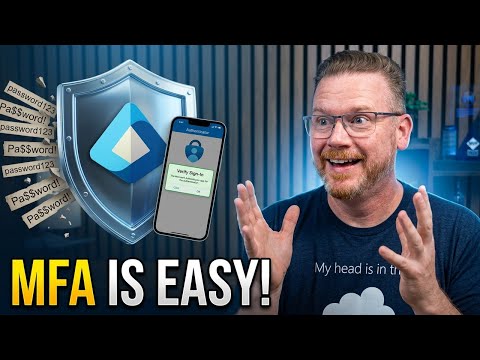
Entra ID MFA: Lock Down M365 & Azure
Secure Microsoft three sixty five with Entra ID MFA, conditional access, Security Defaults and Microsoft Authenticator
Key insights
- The video explains the core problem: Passwords are a single factor and can be stolen by phishing, password spraying, credential stuffing, or reuse.
Attackers who get passwords can access email, files, and cloud resources quickly. - The presenter demonstrates Entra ID (formerly Azure AD) as Microsoft’s cloud identity platform that controls access to Microsoft 365, Azure, apps, and devices.
The demo walks the Entra ID portal to show where admins view sign-ins and apply policies. - The video stresses the value of MFA and shows common methods like the Microsoft Authenticator app, biometrics, passkeys, and security keys.
Microsoft data cited in the video shows accounts with MFA are far less likely to be compromised. - It covers Conditional Access as the policy engine that enforces when to require MFA or block access based on user, app, device, location, or sign-in risk.
Using Conditional Access lets admins apply stronger controls for privileged roles and high-risk sign-ins. - The recording highlights Passwordless and phishing-resistant options such as FIDO2 security keys, passkeys, and Windows Hello for Business as stronger choices than SMS or voice codes.
These methods reduce the chance of successful phishing and credential theft. - The demo recommends immediate steps: enable Security Defaults, review sign-in logs, check the Identity Secure Score, block legacy authentication, and require user MFA registration with the Authenticator app.
These actions provide a fast, practical start toward Zero Trust protection for Microsoft 365 and Azure.
Travis Roberts’s YouTube video, titled Passwords Alone DON'T WORK! Secure M365/Azure with Entra ID MFA!, offers a clear, beginner-friendly introduction to protecting Microsoft 365 and Azure with identity-first controls. In straightforward terms, Roberts explains why relying on a single factor like a password leaves organizations exposed to phishing, password spray, and credential stuffing, and then demonstrates practical steps administrators can take inside the Microsoft Entra ID portal. Consequently, the video serves as a concise starting point for IT pros who need to move from theory to hands-on configuration without prior Entra experience. Overall, the presentation balances high-level rationale with a live demo so viewers can see how controls appear and behave in near real time.
What the video covers
Roberts begins by framing the core problem: passwords are easily compromised, and identity is now the primary perimeter in cloud environments, which makes authentication controls the first line of defense. He then walks through sign-in logs to show authentication attempts and abnormal patterns, and he highlights the Identity Secure Score as a useful baseline to measure improvements. Next, he demonstrates enabling Security Defaults as a quick, built-in way to add multiline protection and finishes with the end-user registration flow using the Microsoft Authenticator app. Thus, the sequence moves logically from problem to tools to user experience, helping IT teams decide what to test first.
Why passwords fail and why MFA matters
Roberts explains that a password is only a single factor and can be stolen through phishing, malware, reuse across breached services, or automated attacks, which makes passwords a fragile defense when used alone. He emphasizes that adding a second factor—such as an authenticator approval, a passkey, or a hardware security key—changes the attacker's calculus and cuts the probability of compromise dramatically. Moreover, Microsoft data cited in the video notes that accounts using multi-factor authentication are far less likely to be breached, so implementing MFA is an evidence-based step for most organizations. Still, Roberts points out that MFA reduces risk rather than eliminating it, so complementary controls remain necessary.
Demonstration of Entra ID tools
In the live demo, Roberts navigates the Entra ID portal to show how sign-in logs reveal near real-time authentication activity and how administrators can investigate suspicious attempts by examining IPs, locations, and device signals. He also reviews the Identity Secure Score, which quantifies an environment's security posture and helps prioritize actions that yield measurable improvements. Then, he enables Security Defaults to illustrate a fast path to baseline protection and walks through the user-facing registration with the Microsoft Authenticator app so readers can understand the end-user journey and common friction points. Therefore, the demo helps bridge theoretical benefits and practical operations, making it easier for teams to adopt the recommended steps.
Balancing security, usability, and investment
Roberts candidly discusses tradeoffs: stronger, phishing-resistant methods like FIDO2 keys and passkeys offer better protection but can increase procurement, onboarding, and support costs for diverse workforces. Conversely, simpler options such as SMS or app-based approvals lower friction and cost but provide weaker resistance to sophisticated attacks, so administrators must weigh risk and user impact. Additionally, blocking legacy authentication and enforcing Conditional Access policies can block many attack vectors, yet they sometimes disrupt legacy apps and require device management or application updates. Therefore, effective deployments balance immediate wins like enabling Security Defaults with longer-term investments in phishing-resistant credentials and device compliance systems.
Challenges and recommended approach
Roberts recommends a phased approach that starts with visibility—reviewing sign-in logs and the secure score—and then moves to enable baseline protections, pilot MFA registration with representative user groups, and expand Conditional Access rules for high-risk roles. He stresses that training and communication reduce user friction during enrollment, while tools like Privileged Identity Management limit standing admin access to reduce blast radius if an account is compromised. At the same time, organizations should plan for edge cases such as emergency access accounts, broken devices, and support workflows so that security does not become a business blocker. In short, Roberts encourages pragmatic steps that raise security steadily while managing operational impacts.
Key takeaways for IT professionals
In conclusion, the video provides a practical roadmap: accept that passwords alone are insufficient, begin with Entra ID visibility and Security Defaults, and then iterate toward Conditional Access and phishing-resistant authentication for critical roles. Roberts’s live walkthrough demystifies the admin console and highlights the balance between quick protective measures and longer-term investments in stronger authentication. Consequently, IT teams that follow this path can reduce the likelihood of account compromise materially while still managing usability and cost tradeoffs. Ultimately, MFA is a foundational step that, paired with monitoring and policy controls, moves organizations closer to a resilient identity posture.
Keywords
Microsoft 365 security, Azure Entra ID MFA, Entra ID multifactor authentication, Passwordless authentication Microsoft, Secure Microsoft 365, Azure AD MFA setup, MFA best practices, Entra ID identity protection