Microsoft Entra ID Passkey Guide
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Microsoft Entra ID passkey guide with Windows Hello for Business, Power Platform and Power BI for passwordless identity
Key insights
- Rapid real-world rollout: Eric led a 600-person organization to deploy passkeys, Windows Hello for Business, and Platform SSO in three months.
He stresses that executive buy-in and strong change management are as important as the technology itself. - Adoption strategies and tooling: The team built a Power Platform self-enrollment portal to let early users "dogfood" the system, moved from voluntary to "voluntold" enrollment, and used Power BI to track adopters and identify stragglers.
They paired automation with clear helpdesk processes to ease the final removal of passwords. - Deployment basics and prerequisites: Admins need the Authentication Policy Administrator role and recent MFA for users to register passkeys.
Hybrid tenants should run Entra Connect and legacy apps may need Application Proxy; supported authenticators include FIDO2 security keys and Microsoft Authenticator. - Passkey profiles and types: Microsoft Entra ID adds passkey profiles with a passkeyType setting to allow device-bound passkeys, synced passkeys, or both.
Attestation enforces device-bound keys only, and Microsoft auto-migrates existing FIDO2 settings into default profiles to simplify rollout. - Security risks to monitor: Passkeys are phishing-resistant, but teams must defend against downgrade attacks that trick users back to passwords and emerging threats like NoAuth, ConsentFix, and Silver SAML.
Protect service principals, monitor consent flows, and document support paths for edge cases. - Practical sign-in and provisioning: Admins enable passkeys in Entra ID authentication policies, issue creationOptions for registration, and provision keys using CTAP-compatible clients.
During sign-in, the authenticator uses public-key cryptography to sign a challenge unlocked by biometric or PIN, and Entra verifies the public key to issue tokens.
Overview of the YouTube conversation
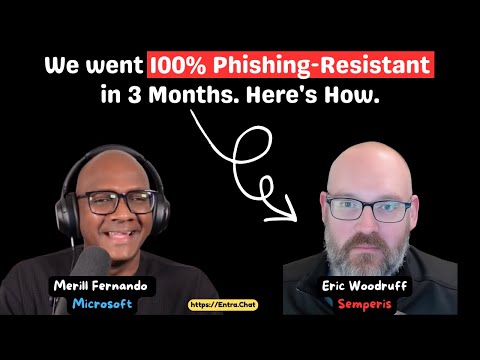
In a recent YouTube episode of EnterChat, host Merill Fernando interviews Eric Woodruff, Chief Identity Architect at Semperis, about a real-world rollout of modern authentication. Over three months, Eric led a 600-person organization through a transition to passkeys, Windows Hello for Business, and Platform SSO, and the discussion centers on practical lessons rather than only technical details. The conversation stresses that achieving a truly phishing-resistant environment depends as much on organizational change as on configuration choices. Therefore, the episode offers a balanced look at both the technical path and the human factors required for success.
Deployment strategy and adoption tactics
Eric explains how his team used a staged approach to encourage adoption, beginning with early adopters who could "dogfood" the solution through a custom self-enrollment portal built on the Power Platform. The portal let volunteers test features and provide feedback, which smoothed the path to wider rollout. Then, in a controlled "voluntold" phase, voluntary participation moved to enforced policy, backed by targeted messaging and automated reminders. Meanwhile, the team used Power BI to measure progress and identify remaining users who needed help, which helped focus support efforts efficiently.
Technical choices and tradeoffs
The episode highlights a key tradeoff between using device-bound passkeys and synced passkeys: device-bound keys offer higher assurance and support attestation, while synced passkeys simplify multi-device use and reduce user friction. Consequently, organizations must weigh security needs against user convenience and decide whether to prioritize strict attestation or broader adoption. In hybrid environments, legacy application exclusions and older devices complicate enforcement, so the team balanced strict policy with targeted exceptions to keep critical services available. Thus, the technical roadmap became a mix of firm security goals and pragmatic allowances for real-world constraints.
Handling device and application challenges
Eric recounts troubleshooting issues with older Android devices and niche browsers that did not fully support modern authentication flows, which required device-specific guidance and temporary workarounds. Additionally, legacy applications that cannot accept modern tokens forced the team to use exclusions or proxies, such as application proxies, while planning phased migrations. These steps introduced operational overhead and required careful documentation to avoid creating new attack surfaces. Therefore, supporting a diverse device fleet demands upfront testing and ongoing operational processes.
Organizational change and support considerations
Beyond the technology, Eric emphasizes that C-suite buy-in and a prepared helpdesk are essential for the "final mile" where passwords are removed entirely. He points out that support staff need scripts, runbooks, and clear escalation paths because users still face issues during and after migration. Moreover, communication campaigns and leader endorsement reduced resistance and improved compliance, showing that human-centered practices accelerate technical outcomes. Ultimately, removing passwords is not a single technical switch but a coordinated program of training, support, and governance.
Security risks and future outlook
The conversation also covers advanced threats, including the risk of downgrade attacks that attempt to trick systems back into using passwords, and research findings like the NoAuth and Silver SAML classes of vulnerabilities that target token and authentication flows. Consequently, organizations must combine passkey deployment with continuous monitoring, token hygiene, and zero trust principles to reduce exposure. Eric recommends documenting processes and keeping an eye on evolving attack techniques while balancing the desire to be passwordless with realistic risk management. In short, the future of enterprise identity is promising, but it requires vigilance, layered defenses, and ongoing operational investment.
In conclusion, the YouTube episode hosted by Merill Fernando and featuring Eric Woodruff provides a practical roadmap for identity modernization: adopt passkeys thoughtfully, plan for diverse device realities, secure executive support, and prepare your helpdesk. By blending technical controls with organizational change, teams can move closer to a truly phishing-resistant environment while managing tradeoffs and operational challenges. Therefore, security leaders should view passkey projects as multidisciplinary efforts that require both technical skill and strong program management.
Keywords
Microsoft Entra ID passkey deployment,passkey deployment best practices,Entra ID passwordless authentication,FIDO2 passkeys Entra ID,Entra ID passkey migration guide,Microsoft Entra identity security,enterprise passkey rollout Entra ID,configure passkeys in Entra ID