Entra Private Access: Ditch Legacy VPNs
Product Manager @ Microsoft 👉 Sign up to Entra.News my weekly newsletter on all things Microsoft Entra | Creator of cmd.ms & idPowerToys.com
Migrate DirectAccess and Always On VPN to Microsoft Entra Private Access with Zero Trust, connector scaling and PKI
Key insights
- Entra Private Access migration works best when done gradually, not in a big bang.
Use a side-by-side approach to replace legacy VPNs so users keep access while you test and tune policies. - Zero Trust demands an identity-first model instead of broad network tunnels.
Enforce Conditional Access and device posture checks so users get only the specific app access they need. - Global Secure Access Client and Private Network Connector are the core components to deploy.
Install the client on endpoints and place connectors on servers with line-of-sight to internal resources to create secure, per-app tunnels. - Plan for capacity and redundancy when scaling Private Network Connectors to avoid service interruptions.
Distribute connectors, monitor load, and test failover to prevent outages during peak use. - Use migration tools and staged patterns to simplify the move: Quick Access for broad coverage, per-app mode for tighter control, and the Zero Trust Network Assessment to find gaps.
Also consider SOA switching to convert synced AD accounts to cloud-managed accounts incrementally. - Track missing features that affect enterprise use: full IPv6 support and process binding are commonly requested, and new capabilities in the Entra E7 suite may change planning.
Keep an eye on roadmap items that influence long-term architecture and compliance.
Overview of the Conversation
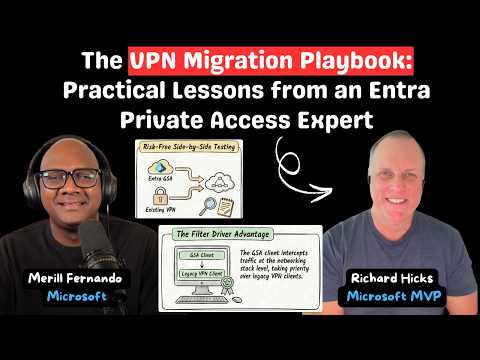
In a recent YouTube discussion hosted by Merill Fernando, Microsoft MVP Richard Hicks lays out practical guidance for organizations moving from legacy VPNs to Entra Private Access. The video examines both strategic decisions and hands-on tactics, and it highlights the operational realities that teams face during migration. Fernando steers the conversation toward real-world tradeoffs, while Hicks draws on more than three decades of secure remote access experience. As a result, viewers gain a grounded view of what a successful migration requires.
Why Zero Trust and Identity-First Access Matter
Hicks emphasizes that traditional VPNs grant broad network access, which conflicts with modern Zero Trust principles that demand least-privilege and continuous verification. Consequently, Entra Private Access shifts enforcement from IP-based networks to identity and device posture, reducing lateral movement risk and narrowing exposure. Moreover, this identity-centric model improves auditability because access ties directly to user and device attributes rather than an opaque tunnel. Therefore, organizations can better align security policy with actual business needs while reducing blast radius.
Migration Strategies and Practical Steps
The video explains that migration does not require a forklift replacement of all legacy systems; instead, teams can run solutions side-by-side while they transition critical services. For example, administrators can use a phased approach that starts with a small set of Fully Qualified Domain Names (FQDNs) or apps via the Global Secure Access Client, and then expand coverage as confidence grows. Additionally, Hicks calls out the value of Quick Access for initial scope and the option to enable per-app access to minimize user disruption during cutover. Thus, the recommended strategy balances continuity with iterative risk reduction.
Technical and Operational Challenges
Despite the advantages, the migration carries nontrivial operational tradeoffs, especially around infrastructure placement and scaling. Hicks warns that Private Network Connectors must be sized and distributed carefully; otherwise, organizations can experience outages or performance bottlenecks if traffic funnels through undersized connectors. Furthermore, administrators must handle device onboarding, conditional access policy tuning, and legacy application compatibility, which together increase project complexity. Consequently, teams must weigh the benefits of tighter security against the upfront engineering effort and potential short-term disruption.
Scaling, Reliability, and the Need to Rethink Networking
Another core theme is how network engineering must evolve from an IP-centric frame of mind to one focused on identity and application affordances. This transition requires retraining and changes in tooling, because many operational processes still assume network-level controls. At the same time, scaling concerns force tradeoffs between centralizing control for simplicity and distributing connectors to improve latency and resilience. Therefore, leaders should plan connector placement, monitoring, and capacity testing early in the migration to avoid surprises during peak load.
Feature Gaps and the Road Ahead
Hicks offers candid commentary on the emerging feature set, praising progress while noting important gaps such as robust IPv6 support and process binding. These missing capabilities can complicate deployments where IPv6 is already in production or where per-process isolation is required for certain legacy apps. In addition, the conversation touches on the newly announced Entra E7 Suite, where Hicks gives measured feedback about what enterprises still need for parity with some mature VPN scenarios. Consequently, organizations should track roadmap items closely and design interim mitigations where necessary.
Balancing Security, Usability, and Cost
Fernando and Hicks repeatedly return to the notion that successful adoption balances security improvements with user experience and operational cost. Implementing strict identity checks and conditional policies improves security, but it can add friction and increase helpdesk tickets if administrators do not phase changes carefully. Likewise, replacing network-centric controls with identity-based controls can reduce attack surface, yet it may require investment in device management and observability. Ultimately, the most sustainable migrations prioritize gradual change, clear communication, and automation to limit administrative overhead.
Recommendations for IT Leaders
To close, the video offers practical recommendations: pilot with a small, representative set of applications, validate connector performance under load, and prepare rollback plans to limit business impact. Moreover, teams should invest in upskilling network and security staff to operate in an identity-first world and track vendor roadmaps for critical features like IPv6 and process binding. In short, careful planning and phased execution allow organizations to reap the security benefits of Entra Private Access while managing the technical and human challenges inherent in any major platform shift.
Keywords
Entra Private Access migration, migrate legacy VPN, replace VPN with Entra Private Access, Entra Private Access guide, Zero Trust Entra migration, VPN to ZTNA migration, SASE vs Entra Private Access, Entra Private Access best practices