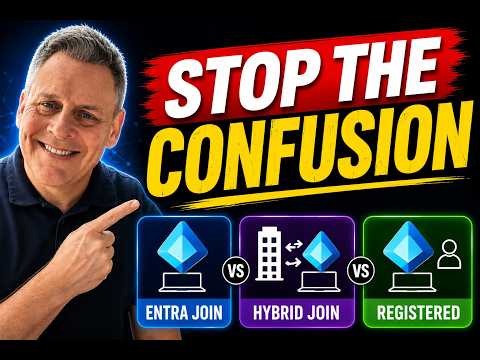
Entra Join vs Hybrid vs Registered
Microsoft 365 Expert, Author, YouTuber, Speaker & Senior Technology Instructor (MCT)
Microsoft expert clears up Entra Join, Hybrid Join and Entra Registered with Intune for cloud first Windows eleven
Key insights
- Entra Joined, Hybrid Entra Joined and Entra Registered are three device identity models from Microsoft.
Entra Joined means the device is cloud‑joined to Entra ID; Hybrid Entra Joined means the device is joined to on‑premises Active Directory and registered with Entra ID; Entra Registered means the device is only registered for app access (typical for BYOD). - Sign-in and management differ by model: Entra Joined uses organizational Entra credentials and supports full cloud management, often with Intune and Windows Autopilot.
Hybrid Entra Joined keeps traditional AD sign-in and Group Policy compatibility while also enabling Entra access; Entra Registered gives limited control and is mainly for app access and Conditional Access checks. - When to choose each: pick Entra Joined for corporate, cloud‑first devices; choose Hybrid Entra Joined if you need on‑prem AD, legacy apps or Group Policy; use Entra Registered for personal/BYOD devices that only need access to corporate apps.
This rule of thumb helps align ownership, security needs and management scope. - Where Intune fits: Intune provides modern device management and complements Entra Joined devices for policies, updates and app deployment.
Hybrid environments can use Intune too, but may require co‑management or AutoPilot adjustments and careful identity sync configuration. - Pros and cons: Entra Joined offers a simpler cloud‑native deployment and faster provisioning; Hybrid Entra Joined preserves legacy controls but adds complexity; Entra Registered minimizes admin control but suits BYOD and reduces user friction.
Weigh operational complexity, security needs and device ownership before deciding. - Best practices and common mistakes: don’t treat registration as a lighter form of join—registration is not a substitute for device management.
Assess device ownership, test configurations, use Conditional Access and compliance policies, and document the chosen model to avoid identity and management gaps.
Introduction to the video
In a recent YouTube presentation, Andy Malone [MVP] clarifies the often-misunderstood device identity choices available from Microsoft: Entra Joined, Hybrid Joined and Entra Registered. He walks viewers through how each option works, where Microsoft Intune fits, and the practical outcomes of choosing one model over another. Consequently, the video aims to help administrators stop the confusion and pick the right approach for their organization.
Moreover, Malone frames the discussion around common migration patterns such as moving away from on-premises infrastructure, adopting Windows 11, and implementing cloud-first device strategies. He uses clear examples and demonstrations to show what happens during enrollment, sign-in, and policy application. Therefore, the presentation suits both teams planning a migration and administrators reviewing their current device estate.
How each join model works
First, Entra Joined describes devices that register directly with Entra ID and are managed in the cloud, which makes them natural candidates for full management with Microsoft Intune and Autopilot. Second, Hybrid Joined devices remain joined to on-premises Active Directory while also registering with Entra ID, letting organizations keep legacy controls like Group Policy. Third, Entra Registered is a lightweight identity model for personal or BYOD devices, where the device is known to the directory but managed only minimally.
Malone emphasizes that registration is not a watered-down join; rather, it serves a different purpose focused on access and Conditional Access policies. He also demonstrates the login flows and where cloud tokens versus on-premises authentication are used, which helps clarify what resources remain dependent on local infrastructure. As a result, viewers can better predict user experience and policy coverage for each model.
Tradeoffs: control, complexity and user experience
The video highlights tradeoffs between control and simplicity: moving to Entra Joined often reduces on-premises complexity but requires strong cloud management practices and planning for Autopilot and enrollment. Conversely, Hybrid Joined preserves legacy investments and allows continued use of Group Policy, yet it introduces extra operational overhead and hybrid identity complexity. Therefore, teams must weigh the cost of keeping on-premises systems against the work needed to modernize.
Furthermore, Malone discusses user experience and privacy tradeoffs related to BYOD scenarios with Entra Registered. While registration gives access control without full device takeover, it also limits the organization’s ability to enforce device-wide security settings. Consequently, security teams face a choice between protecting corporate data and respecting user control on personal devices, which often leads to mixed models within the same organization.
Challenges in deployment and management
Malone walks through real challenges such as conditional access gaps, legacy authentication, and devices that must access on-premises resources like file shares or domain-joined services. These scenarios often force hybrid designs, which can complicate troubleshooting because administrators must track policies and certificates across two identity systems. As a result, planning for certificate distribution, hybrid join automation and token lifetimes becomes critical in hybrid environments.
Another common challenge the video highlights is migration sequencing and user impact during transitions, especially when moving large fleets to Entra Joined or enabling Intune enrollment. Malone recommends staged rollouts, pilot groups, and clear communication to reduce disruption. Therefore, organizations should budget time for testing, script refinement, and user education to avoid helpdesk overload during change windows.
Best practices and common mistakes
In practical terms, Malone suggests following a few core practices: define device ownership policies, align management tooling with those policies, and pilot each join model before a broad rollout. He also recommends documenting exceptions, such as devices that require legacy authentication, and automating where possible to maintain consistency. Consequently, these steps help reduce lifecycle issues and enforcement gaps that often arise in mixed environments.
He calls out common mistakes, including treating Entra Registered as a light join for corporate devices, skipping pilot phases, and not accounting for on-premises dependencies early enough. Therefore, teams should avoid one-size-fits-all decisions and instead map device types to join models based on ownership, access needs, and compliance. With careful planning, organizations can balance security, user experience and administrative effort more effectively.
Choosing the right approach
Finally, Malone offers a simple decision framework: use Entra Joined for cloud-first corporate devices, choose Hybrid Joined where on-premises controls remain essential, and adopt Entra Registered for BYOD scenarios that require access without full management. He stresses that these choices are not permanent; organizations can migrate devices as their needs evolve, but they must plan the migration path. Consequently, the video serves as a practical guide rather than a prescriptive mandate.
Overall, the presentation delivers clear distinctions and pragmatic advice that administrators can act on immediately. By comparing user experience, management scope and operational complexity, Andy Malone [MVP] helps organizations make informed decisions that match their technical and organizational constraints. Therefore, IT leaders should view the video as a useful tool when designing or revising their device strategy.
Keywords
Entra Join vs Hybrid Join,Hybrid Azure AD Join,Azure AD registered devices,Entra ID device registration,Azure AD Join vs Hybrid Join,Windows Autopilot Entra Join,Entra Registered vs Joined,Entra Join tutorial