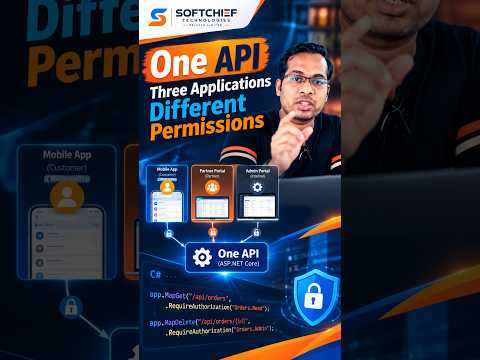
ASP.NET Core API security separates app permissions
Learn how to take advantage of your business data with Microsoft Dynamics 365 & Power Platform & Cross Technologies. My name is Sanjaya Prakash Pradhan and I am a Microsoft Certified Trainer (MCT) and
Softchief Learn highlights one API serving three apps with different access, a pattern that helps teams avoid giving every client the same permissions.
Key insights
- The Short is titled “One API, Three Apps, Different Permissions” and concerns ASP.NET Core API security.
- Delegated permissions apply when an app acts for a signed-in user; application permissions cover app-only access.
- The research notes describe scopes in the scp claim and application permissions in the roles claim.
- ASP.NET Core can validate bearer tokens and apply authorization rules based on claims and policies.
- The Short’s description contains no transcript or implementation details, so its exact demonstration is unclear.
Softchief Learn recently published a YouTube Short titled “One API, Three Apps, Different Permissions,” focused on ASP.NET Core API security. Its central idea is that several applications can call one API without receiving identical access. The accompanying Short description contains no transcript, so the specific steps shown in the video cannot be confirmed.
What's new
The title points to a familiar API design problem: a web app, mobile app, and background service may all need the same API, but not the same privileges. The research notes describe Microsoft Entra ID issuing access tokens and an ASP.NET Core API checking their claims before allowing a request. They distinguish user-delegated scopes from application permissions used when no user is present.
For example, a user-facing client might request an `Orders.Read` scope, while a mobile app could also need `Orders.Write`. A background service might instead use an application role such as `Orders.Read.All`. These are examples in the research notes, not confirmed names or configurations shown in the Short.
Why it matters
For API developers and architects, separate permissions can prevent a client that only needs to read data from also receiving write access. The distinction also helps teams reason about who is making a request: a user through an app, or an application acting on its own. Authentication establishes the caller’s identity; authorization determines what that caller can do.
Admins and identity teams may be involved in registering the API and its clients and granting permissions. The notes describe API-defined scopes and roles, with approved permissions represented in access tokens. They do not specify licensing, rollout status, or any tenant-wide availability conditions.
How it works
The research describes a flow in which Microsoft Entra ID issues an access token to a client, which sends it to the API as a bearer token. ASP.NET Core’s JWT bearer handler validates the token, and authorization logic checks its claims. A user-driven request typically uses the `scp` claim for delegated scopes, while an app-only request typically uses the `roles` claim.
- Register the API and client applications, then define the permissions the API exposes.
- Have each client request or receive only the permissions it needs.
- Validate incoming tokens and enforce access rules in the API, such as with authorization policies.
The research notes identify Microsoft.Identity.Web as one library used to integrate ASP.NET Core with the Microsoft identity platform. The Short description does not confirm whether the video uses this library or walks through these setup steps.
Limitations and open questions
The available video description consists only of a brief label, and the supplied research notes provide context rather than a verifiable transcript of the clip. That means the exact apps, code, configuration, and permission names used in the video are unknown. Readers should treat the examples here as background, not as a record of the Short’s on-screen implementation.
The sources also do not establish which ASP.NET Core version or deployment environment the video uses. The Short’s title alone cannot confirm whether it demonstrates a working configuration or covers token validation edge cases. Consult the linked material for the original clip and publisher context.
Sources
Frequently asked questions
Can one ASP.NET Core API give different apps different access?
Yes. The research notes describe using delegated scopes and application roles so clients can receive distinct permissions. The Short’s description does not show the specific configuration.
What is the difference between delegated and application permissions?
Delegated permissions apply when an app acts on behalf of a signed-in user. Application permissions are for an app acting without a user, such as a background service.
Does the Short include code or a setup walkthrough?
The available description has no transcript or implementation details, so that cannot be confirmed.